Google redirect problem

platypus

New Member
Hello, I've been experiencing a problem where clicking links for Google search results keep getting redirected to random websites. Additionally, every once in a while a new tab will pop up with a false Google website with something like "webhp" tacked onto the end of the address.

Any help I could get in removing this nasty little bug would be very greatly appreciated.

Here are my Malwarebytes and HijackThis logs:

Malwarebytes' Anti-Malware 1.46
www.malwarebytes.org

Database version: 4896

Windows 5.1.2600 Service Pack 3
Internet Explorer 6.0.2900.5512

10/20/2010 7:09:35 PM
mbam-log-2010-10-20 (19-09-35).txt

Scan type: Quick scan
Objects scanned: 156013
Time elapsed: 14 minute(s), 33 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 0
Registry Values Infected: 0
Registry Data Items Infected: 0
Folders Infected: 0
Files Infected: 3

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
(No malicious items detected)

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
(No malicious items detected)

Folders Infected:
(No malicious items detected)

Files Infected:
C:\Documents and Settings\MegaeraJ\Application Data\asdsada.bat (Malware.Trace) -> Quarantined and deleted successfully.
C:\Documents and Settings\MegaeraJ\Application Data\444.bat (Malware.Trace) -> Quarantined and deleted successfully.
C:\Documents and Settings\MegaeraJ\Application Data\srsf.bat (Malware.Trace) -> Quarantined and deleted successfully.


Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 6:49:17 PM, on 10/20/2010
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP3 (6.00.2900.5512)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\csrss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\WTouch\WTouchService.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\WLTRYSVC.EXE
C:\WINDOWS\System32\bcmwltry.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\Program Files\Spyware Doctor\BDT\BDTUpdateService.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\Program Files\Autodesk\3ds Max 9\mentalray\satellite\raysat_3dsmax9_32server.exe
C:\Program Files\Super_DVD_Creator_9.8\NMSAccessU.exe
C:\WINDOWS\system32\nvsvc32.exe
C:\Softimage\XSI_5.11\Application\bin\raysat3_4_6_18server.exe
C:\Program Files\Spyware Doctor\pctsAuxs.exe
C:\Program Files\Spyware Doctor\pctsSvc.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\Tablet.exe
C:\Program Files\Spyware Doctor\pctsTray.exe
C:\WINDOWS\system32\Pen_Tablet.exe
C:\Program Files\Viewpoint\Common\ViewpointService.exe
C:\WINDOWS\system32\dla\tfswctrl.exe
C:\WINDOWS\system32\WLTRAY.exe
C:\WINDOWS\system32\rundll32.exe
C:\Program Files\SigmaTel\C-Major Audio\WDM\stsystra.exe
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Common Files\Java\Java Update\jusched.exe
C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
C:\Program Files\DNA\btdna.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\McAfee Security Scan\2.0.181\SSScheduler.exe
C:\Program Files\MagicDisc\MagicDisc.exe
C:\Program Files\iTunes\iTunes.exe
C:\WINDOWS\system32\WTablet\TabUserW.exe
C:\WINDOWS\system32\Tablet.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceHelper.exe
C:\WINDOWS\System32\alg.exe
C:\Program Files\Common Files\Apple\Apple Application Support\distnoted.exe
C:\WINDOWS\System32\mshta.exe
C:\Program Files\WTouch\WTouchUser.exe
C:\WINDOWS\System32\mshta.exe
C:\WINDOWS\system32\wuauclt.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\wuauclt.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Program Files\Mozilla Firefox\plugin-container.exe
C:\WINDOWS\system32\msiexec.exe
C:\Program Files\Trend Micro\HiJackThis\HiJackThis.exe
C:\WINDOWS\system32\wbem\wmiprvse.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.dvdcopyrip.com
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
R3 - URLSearchHook: AIM Toolbar Search Class - {03402f96-3dc7-4285-bc50-9e81fefafe43} - C:\Program Files\AIM Toolbar\aimtb.dll
R3 - URLSearchHook: AOLSearchHook Class - {54EB34EA-E6BE-4CFD-9F4F-C4A0C2EAFA22} - C:\Program Files\AIM Search\AOLSearch.dll
O1 - Hosts: # Copyright (c) 1993-1999 Microsoft Corp.
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: Browser Defender BHO - {2A0F3D1B-0909-4FF4-B272-609CCE6054E7} - C:\Program Files\Spyware Doctor\BDT\PCTBrowserDefender.dll
O2 - BHO: Spybot-S&D IE Protection - {53707962-6F74-2D53-2644-206D7942484F} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O2 - BHO: AOL Search Enhancement - {54EB34EA-E6BE-4CFD-9F4F-C4A0C2EAFA22} - C:\Program Files\AIM Search\AOLSearch.dll
O2 - BHO: DriveLetterAccess - {5CA3D70E-1895-11CF-8E15-001234567890} - C:\WINDOWS\system32\dla\tfswshx.dll
O2 - BHO: AIM Toolbar Loader - {b0cda128-b425-4eef-a174-61a11ac5dbf8} - C:\Program Files\AIM Toolbar\aimtb.dll
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: AIM Toolbar - {61539ecd-cc67-4437-a03c-9aaccbd14326} - C:\Program Files\AIM Toolbar\aimtb.dll
O3 - Toolbar: PC Tools Browser Guard - {472734EA-242A-422B-ADF8-83D1E48CC825} - C:\Program Files\Spyware Doctor\BDT\PCTBrowserDefender.dll
O4 - HKLM\..\Run: [dla] C:\WINDOWS\system32\dla\tfswctrl.exe
O4 - HKLM\..\Run: [Broadcom Wireless Manager UI] C:\WINDOWS\system32\WLTRAY.exe
O4 - HKLM\..\Run: [NvCplDaemon] RUNDLL32.EXE C:\WINDOWS\system32\NvCpl.dll,NvStartup
O4 - HKLM\..\Run: [nwiz] nwiz.exe /installquiet
O4 - HKLM\..\Run: [NVHotkey] rundll32.exe nvHotkey.dll,Start
O4 - HKLM\..\Run: [SigmatelSysTrayApp] %ProgramFiles%\SigmaTel\C-Major Audio\WDM\stsystra.exe
O4 - HKLM\..\Run: [SynTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
O4 - HKLM\..\Run: [IMJPMIG8.1] "C:\WINDOWS\IME\imjp8_1\IMJPMIG.EXE" /Spoil /RemAdvDef /Migration32
O4 - HKLM\..\Run: [MSPY2002] C:\WINDOWS\system32\IME\PINTLGNT\ImScInst.exe /SYNC
O4 - HKLM\..\Run: [PHIME2002ASync] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /SYNC
O4 - HKLM\..\Run: [PHIME2002A] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /IMEName
O4 - HKLM\..\Run: [ISTray] "C:\Program Files\Spyware Doctor\pctsTray.exe"
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKLM\..\Run: [AdobeCS4ServiceManager] "C:\Program Files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\QTTask.exe" -atboottime
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKCU\..\Run: [BitTorrent DNA] "C:\Program Files\DNA\btdna.exe"
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [Google Update] "C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe" /c
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O4 - Startup: MagicDisc.lnk = C:\Program Files\MagicDisc\MagicDisc.exe
O4 - Global Startup: McAfee Security Scan Plus.lnk = ?
O4 - Global Startup: Microsoft Office.lnk = C:\Program Files\Microsoft Office\Office10\OSA.EXE
O4 - Global Startup: TabUserW.exe.lnk = C:\WINDOWS\system32\WTablet\TabUserW.exe
O8 - Extra context menu item: &AIM Toolbar Search - C:\Documents and Settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~3\Office10\EXCEL.EXE/3000
O8 - Extra context menu item: Free YouTube Download - C:\Documents and Settings\MegaeraJ\Application Data\DVDVideoSoftIEHelpers\youtubedownload.htm
O9 - Extra button: AIM Toolbar - {0b83c99c-1efa-4259-858f-bcb33e007a5b} - C:\Program Files\AIM Toolbar\aimtb.dll
O9 - Extra button: (no name) - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra 'Tools' menuitem: Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
O23 - Service: Autodesk Licensing Service - Autodesk - C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: Browser Defender Update Service - Unknown owner - C:\Program Files\Spyware Doctor\BDT\BDTUpdateService.exe
O23 - Service: FLEXnet Licensing Service - Acresso Software Inc. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: Lavasoft Ad-Aware Service - Lavasoft - C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe
O23 - Service: McAfee Security Scan Component Host Service (McComponentHostService) - McAfee, Inc. - C:\Program Files\McAfee Security Scan\2.0.181\McCHSvc.exe
O23 - Service: mental ray 3.5 Satellite (32-bit) (mi-raysat_3dsmax9_32) - Unknown owner - C:\Program Files\Autodesk\3ds Max 9\mentalray\satellite\raysat_3dsmax9_32server.exe
O23 - Service: NMSAccessU - Unknown owner - C:\Program Files\Super_DVD_Creator_9.8\NMSAccessU.exe
O23 - Service: NVIDIA Display Driver Service (NVSvc) - NVIDIA Corporation - C:\WINDOWS\system32\nvsvc32.exe
O23 - Service: RaySat3_4_6_18 Server (RaySat3_4_6_18Server) - Unknown owner - C:\Softimage\XSI_5.11\Application\bin\raysat3_4_6_18server.exe
O23 - Service: PC Tools Auxiliary Service (sdAuxService) - PC Tools - C:\Program Files\Spyware Doctor\pctsAuxs.exe
O23 - Service: PC Tools Security Service (sdCoreService) - PC Tools - C:\Program Files\Spyware Doctor\pctsSvc.exe
O23 - Service: SPM License Server (spmd) - Unknown owner - C:\WINDOWS\system32\spm\spmd.exe (file missing)
O23 - Service: TabletService - Wacom Technology, Corp. - C:\WINDOWS\system32\Tablet.exe
O23 - Service: TabletServicePen - Wacom Technology, Corp. - C:\WINDOWS\system32\Pen_Tablet.exe
O23 - Service: Viewpoint Manager Service - Viewpoint Corporation - C:\Program Files\Viewpoint\Common\ViewpointService.exe
O23 - Service: Dell Wireless WLAN Tray Service (wltrysvc) - Unknown owner - C:\WINDOWS\System32\WLTRYSVC.EXE
O23 - Service: WTouch Service (WTouchService) - Wacom Technology, Corp. - C:\Program Files\WTouch\WTouchService.exe

--
End of file - 11382 bytes
 
Ok, first thing...

Rerun hijackthis and place checks next to the following entries.

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.dvdcopyrip.com/
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Int ernet Settings,ProxyOverride = *.local
R3 - URLSearchHook: AIM Toolbar Search Class - {03402f96-3dc7-4285-bc50-9e81fefafe43} - C:\Program Files\AIM Toolbar\aimtb.dll
R3 - URLSearchHook: AOLSearchHook Class - {54EB34EA-E6BE-4CFD-9F4F-C4A0C2EAFA22} - C:\Program Files\AIM Search\AOLSearch.dll
O1 - Hosts: # Copyright (c) 1993-1999 Microsoft Corp.
O2 - BHO: AIM Toolbar Loader - {b0cda128-b425-4eef-a174-61a11ac5dbf8} - C:\Program Files\AIM Toolbar\aimtb.dll
O3 - Toolbar: AIM Toolbar - {61539ecd-cc67-4437-a03c-9aaccbd14326} - C:\Program Files\AIM Toolbar\aimtb.dll
O4 - HKLM\..\Run: [IMJPMIG8.1] "C:\WINDOWS\IME\imjp8_1\IMJPMIG.EXE" /Spoil /RemAdvDef /Migration32
O4 - HKLM\..\Run: [MSPY2002] C:\WINDOWS\system32\IME\PINTLGNT\ImScInst.exe /SYNC
O4 - HKLM\..\Run: [PHIME2002ASync] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /SYNC
O4 - HKLM\..\Run: [PHIME2002A] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /IMEName
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKLM\..\Run: [AdobeCS4ServiceManager] "C:\Program Files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.ex e" -launchedbylogin
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\QTTask.exe" -atboottime
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKCU\..\Run: [BitTorrent DNA] "C:\Program Files\DNA\btdna.exe"
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [Google Update] "C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe" /c
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O4 - Global Startup: McAfee Security Scan Plus.lnk = ?
O4 - Global Startup: Microsoft Office.lnk = C:\Program Files\Microsoft Office\Office10\OSA.EXE

Then click on fix checked at the bottom.

Please post an uninstall list using hijackthis. Open hijackthis, click on open misc tools section, click on open uninstall manager, click on save list and save it, then copy and paste the log back here.

Then perform the following procedure.

Download and Run ComboFix
If you already have Combofix, please delete this copy and download it again as it's being updated regularly.
Note: Do not mouseclick combofix's window whilst it's running. That may cause it to stall

Combofix should never take more that 20 minutes including the reboot if malware is detected.


In your next reply please post:
  • The Uninstall log
  • The ComboFix log
  • A fresh HiJackThis log
  • An update on how your computer is running
 
Hello,

I followed your instructions and ran into some interesting predicaments along the way. When I was finishing up getting the Uninstall Log, I got a pop-up about McAfee security scanner running a scan and an icon for McAfee Security Scan Plus appeared on my desktop.

I have no memory of ever downloading any manner of McAfee spyware removal and I'm not sure if it is part of the infection.

After it showed up the computer started running extremely slow and finally froze before I could install ComboFix. When I restarted the computer I was able to successfully install and run Combo fix and get all of the logs.

The redirects are still occurring and Firefox closed on me a few times in favor of pop-ups made to look like error messages about needing urgent spyware removal treatment.

Also Internet Explorer decided to put an icon on my desktop.

Here are all of the log:

Uninstall List

3dsmax ancillary install
3ivx MPEG-4 5.0.1 Decoder (remove only)
7-Zip 4.57
Acrobat.com
Acrobat.com
Ad-Aware
Ad-Aware
Ad-Aware Email Scanner for Outlook
Adobe After Effects CS3
Adobe After Effects CS3 Presets
Adobe AIR
Adobe AIR
Adobe Anchor Service CS3
Adobe Anchor Service CS4
Adobe Asset Services CS3
Adobe Bridge 1.0
Adobe Bridge CS3
Adobe Bridge CS4
Adobe Bridge Start Meeting
Adobe Camera Raw 4.0
Adobe CMaps CS4
Adobe Color - Photoshop Specific
Adobe Color EU Extra Settings CS4
Adobe Color JA Extra Settings CS4
Adobe Color NA Recommended Settings CS4
Adobe Common File Installer
Adobe CSI CS4
Adobe Default Language CS4
Adobe Device Central CS3
Adobe Device Central CS4
Adobe Drive CS4
Adobe Dynamiclink Support
Adobe ExtendScript Toolkit 2
Adobe ExtendScript Toolkit CS4
Adobe Extension Manager CS4
Adobe Flash CS4
Adobe Flash CS4 Extension - Flash Lite STI en
Adobe Flash CS4 Professional
Adobe Flash CS4 STI-en
Adobe Flash Player 10 ActiveX
Adobe Flash Player 10 Plugin
Adobe Fonts All
Adobe Help Center 1.0
Adobe Help Viewer CS3
Adobe Illustrator CS3
Adobe Linguistics CS3
Adobe Linguistics CS4
Adobe Media Encoder CS4
Adobe Media Encoder CS4 Importer
Adobe Media Player
Adobe Media Player
Adobe MotionPicture Color Files
Adobe Output Module
Adobe PDF Library Files CS4
Adobe Photoshop CS2
Adobe Reader 9.3.4
Adobe Search for Help
Adobe Service Manager Extension
Adobe Setup
Adobe Setup
Adobe Setup
Adobe Shockwave Player 11.5
Adobe Stock Photos 1.0
Adobe Stock Photos CS3
Adobe Type Support CS4
Adobe Update Manager CS3
Adobe Update Manager CS4
Adobe Version Cue CS3 Client
Adobe Video Profiles
Adobe WinSoft Linguistics Plugin
Adobe XMP DVA Panels CS3
Adobe XMP Panels CS3
Adobe XMP Panels CS4
AdobeColorCommonSetCMYK
AdobeColorCommonSetRGB
AIM 6
AIM Search
AIM Toolbar
Akamai NetSession Interface
Apophysis 2.0
Apple Application Support
Apple Mobile Device Support
Apple Software Update
Autodesk 3ds Max 9 32-bit
Autodesk DWF Viewer 7
Backburner
BitPim 1.0.6
Bonjour
Browser Defender 2.0.6.15
CDisplay 1.8
Compatibility Pack for the 2007 Office system
Conexant HDA D110 MDC V.92 Modem
Connect
Crayon Physics Deluxe Demo - release 52
Critical Update for Windows Media Player 11 (KB959772)
Cucusoft YouTube Mate 7.12
Dell ResourceCD
Dell Wireless WLAN Card
DirectVobSub (remove only)
DoremiSoft AVI to MP4 Converter 1.0
Download Updater (AOL LLC)
FBX Plugin 2006.08 for Max 9.0
FileZilla Client 3.2.4.1
Free DVD Creator
Free MKV Video2Dvd 2.81
Free Studio version 4.2
Free YouTube Download 2.9
Guild Wars
Haihaisoft Universal Player
High Definition Audio Driver Package - KB835221
HiJackThis
Hitman Pro 3.5
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595)
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484)
Hotfix for Windows Media Format 11 SDK (KB929399)
Hotfix for Windows Media Player 11 (KB939683)
Hotfix for Windows XP (KB2158563)
Hotfix for Windows XP (KB952287)
Hotfix for Windows XP (KB961118)
Hotfix for Windows XP (KB970653-v3)
Hotfix for Windows XP (KB976098-v2)
Hotfix for Windows XP (KB979306)
Hotfix for Windows XP (KB981793)
iTunes
Java(TM) 6 Update 21
K-Lite Mega Codec Pack 3.7.5
kuler
LG USB Modem driver
Macromedia Extension Manager
Macromedia Flash 8 Video Encoder
Magic ISO Maker v5.5 (build 0274)
MagicDisc 2.7.106
Malwarebytes' Anti-Malware
McAfee Security Scan Plus
Microangelo Toolset 6
Microsoft .NET Framework 1.1
Microsoft .NET Framework 1.1 Security Update (KB2416447)
Microsoft .NET Framework 1.1 Security Update (KB979906)
Microsoft .NET Framework 2.0 Service Pack 2
Microsoft .NET Framework 3.0 Service Pack 2
Microsoft .NET Framework 3.5 SP1
Microsoft Compression Client Pack 1.0 for Windows XP
Microsoft Office XP Small Business
Microsoft SQL Server Desktop Engine (SONY_MEDIAMGR)
Microsoft User-Mode Driver Framework Feature Pack 1.0
Microsoft VC9 runtime libraries
Microsoft Visual C++ 2005 Redistributable
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17
Mozilla Firefox (3.6.11)
MSXML 6.0 Parser (KB925673)
muvee Plugin 1.0
NVIDIA Drivers
OpenAL
Pando Media Booster
PDF Settings CS4
PeerGuardian 2.0
Pen Tablet
PENTAX USB DISK Device
Photoshop Camera Raw
Pixel Bender Toolkit
PowerDVD 5.3
QuickTime
Roll
Rosetta Stone Version 3
Security Update for Microsoft .NET Framework 3.5 SP1 (KB2416473)
Security Update for Windows Media Player (KB2378111)
Security Update for Windows Media Player (KB952069)
Security Update for Windows Media Player (KB954155)
Security Update for Windows Media Player (KB968816)
Security Update for Windows Media Player (KB973540)
Security Update for Windows Media Player (KB975558)
Security Update for Windows Media Player (KB978695)
Security Update for Windows Media Player 11 (KB936782)
Security Update for Windows Media Player 11 (KB954154)
Security Update for Windows XP (KB2079403)
Security Update for Windows XP (KB2115168)
Security Update for Windows XP (KB2121546)
Security Update for Windows XP (KB2160329)
Security Update for Windows XP (KB2183461)
Security Update for Windows XP (KB2229593)
Security Update for Windows XP (KB2259922)
Security Update for Windows XP (KB2279986)
Security Update for Windows XP (KB2286198)
Security Update for Windows XP (KB2296011)
Security Update for Windows XP (KB2347290)
Security Update for Windows XP (KB2360131)
Security Update for Windows XP (KB2360937)
Security Update for Windows XP (KB2387149)
Security Update for Windows XP (KB923561)
Security Update for Windows XP (KB923789)
Security Update for Windows XP (KB938464)
Security Update for Windows XP (KB941569)
Security Update for Windows XP (KB946648)
Security Update for Windows XP (KB950759)
Security Update for Windows XP (KB950760)
Security Update for Windows XP (KB950762)
Security Update for Windows XP (KB950974)
Security Update for Windows XP (KB951066)
Security Update for Windows XP (KB951376-v2)
Security Update for Windows XP (KB951698)
Security Update for Windows XP (KB951748)
Security Update for Windows XP (KB952004)
Security Update for Windows XP (KB952954)
Security Update for Windows XP (KB953838)
Security Update for Windows XP (KB953839)
Security Update for Windows XP (KB954211)
Security Update for Windows XP (KB954459)
Security Update for Windows XP (KB954600)
Security Update for Windows XP (KB955069)
Security Update for Windows XP (KB956390)
Security Update for Windows XP (KB956391)
Security Update for Windows XP (KB956572)
Security Update for Windows XP (KB956744)
Security Update for Windows XP (KB956802)
Security Update for Windows XP (KB956803)
Security Update for Windows XP (KB956841)
Security Update for Windows XP (KB956844)
Security Update for Windows XP (KB957095)
Security Update for Windows XP (KB957097)
Security Update for Windows XP (KB958215)
Security Update for Windows XP (KB958644)
Security Update for Windows XP (KB958687)
Security Update for Windows XP (KB958690)
Security Update for Windows XP (KB958869)
Security Update for Windows XP (KB959426)
Security Update for Windows XP (KB960225)
Security Update for Windows XP (KB960714)
Security Update for Windows XP (KB960715)
Security Update for Windows XP (KB960803)
Security Update for Windows XP (KB960859)
Security Update for Windows XP (KB961371-v2)
Security Update for Windows XP (KB961373)
Security Update for Windows XP (KB961501)
Security Update for Windows XP (KB963027)
Security Update for Windows XP (KB968537)
Security Update for Windows XP (KB969059)
Security Update for Windows XP (KB969897)
Security Update for Windows XP (KB969898)
Security Update for Windows XP (KB969947)
Security Update for Windows XP (KB970238)
Security Update for Windows XP (KB970430)
Security Update for Windows XP (KB971468)
Security Update for Windows XP (KB971486)
Security Update for Windows XP (KB971557)
Security Update for Windows XP (KB971633)
Security Update for Windows XP (KB971657)
Security Update for Windows XP (KB971961)
Security Update for Windows XP (KB972260)
Security Update for Windows XP (KB972270)
Security Update for Windows XP (KB973346)
Security Update for Windows XP (KB973354)
Security Update for Windows XP (KB973507)
Security Update for Windows XP (KB973525)
Security Update for Windows XP (KB973869)
Security Update for Windows XP (KB973904)
Security Update for Windows XP (KB974112)
Security Update for Windows XP (KB974318)
Security Update for Windows XP (KB974392)
Security Update for Windows XP (KB974455)
Security Update for Windows XP (KB974571)
Security Update for Windows XP (KB975025)
Security Update for Windows XP (KB975467)
Security Update for Windows XP (KB975560)
Security Update for Windows XP (KB975561)
Security Update for Windows XP (KB975562)
Security Update for Windows XP (KB975713)
Security Update for Windows XP (KB977165-v2)
Security Update for Windows XP (KB977816)
Security Update for Windows XP (KB977914)
Security Update for Windows XP (KB978037)
Security Update for Windows XP (KB978251)
Security Update for Windows XP (KB978262)
Security Update for Windows XP (KB978338)
Security Update for Windows XP (KB978542)
Security Update for Windows XP (KB978601)
Security Update for Windows XP (KB978706)
Security Update for Windows XP (KB979309)
Security Update for Windows XP (KB979482)
Security Update for Windows XP (KB979559)
Security Update for Windows XP (KB979683)
Security Update for Windows XP (KB979687)
Security Update for Windows XP (KB980195)
Security Update for Windows XP (KB980218)
Security Update for Windows XP (KB980232)
Security Update for Windows XP (KB980436)
Security Update for Windows XP (KB981322)
Security Update for Windows XP (KB981349)
Security Update for Windows XP (KB981852)
Security Update for Windows XP (KB981957)
Security Update for Windows XP (KB981997)
Security Update for Windows XP (KB982132)
Security Update for Windows XP (KB982214)
Security Update for Windows XP (KB982381)
Security Update for Windows XP (KB982665)
Security Update for Windows XP (KB982802)
SigmaTel Audio
SOFTIMAGE®|XSI® 5.11
Sonic DLA
Sonic MyDVD
Sonic RecordNow!
Sonic Update Manager
Sony Media Manager 2.2
Sony Vegas 7.0a
Spelling Dictionaries Support For Adobe Reader 9
SPM License Server 1.1.11-1307
Spybot - Search & Destroy
Spyware Doctor 7.0
Starcraft
Suite Shared Configuration CS4
Super DVD Creator 9.8 Trial Version
Synaptics Pointing Device Driver
Tablet
TubeTilla Free
Ultra Fractal 5.01 Standard Edition
Ultra RM Converter 4.2.0104
Uninstall 1.0.0.1
Update for Microsoft .NET Framework 3.5 SP1 (KB963707)
Update for Windows XP (KB2141007)
Update for Windows XP (KB2345886)
Update for Windows XP (KB942763)
Update for Windows XP (KB951072-v2)
Update for Windows XP (KB951978)
Update for Windows XP (KB955759)
Update for Windows XP (KB955839)
Update for Windows XP (KB967715)
Update for Windows XP (KB968389)
Update for Windows XP (KB971737)
Update for Windows XP (KB973687)
Update for Windows XP (KB973815)
Update for Windows XP (KB976749)
Update for Windows XP (KB980182)
VideoLAN VLC media player 0.8.6i
Viewpoint Media Player
Visual C++ 2008 x86 Runtime - (v9.0.30729)
Visual C++ 2008 x86 Runtime - v9.0.30729.01
vixy converter uninstall
Vue 6 Infinite PLE 32bit
WebTablet IE Plugin
WebTablet Netscape Plugin
Windows Installer Clean Up
Windows Media Format 11 runtime
Windows Media Player 11
Windows Presentation Foundation
Windows XP Service Pack 3
World of Goo
Xfire (remove only)
X-Men(TM) Legends 2
Xvid 1.2.1 final uninstall
YASA MP4 Video Converter v3.2 (build 0051)


ComboFix 10-10-20.01 - MegaeraJ 10/21/2010 2:07.1.2 - x86
Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.1022.558 [GMT -4:00]
Running from: c:\documents and settings\MegaeraJ\Desktop\ComboFix.exe
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

c:\windows\Tasks\At1.job
c:\windows\Tasks\At10.job
c:\windows\Tasks\At11.job
c:\windows\Tasks\At12.job
c:\windows\Tasks\At13.job
c:\windows\Tasks\At14.job
c:\windows\Tasks\At15.job
c:\windows\Tasks\At16.job
c:\windows\Tasks\At17.job
c:\windows\Tasks\At18.job
c:\windows\Tasks\At19.job
c:\windows\Tasks\At2.job
c:\windows\Tasks\At20.job
c:\windows\Tasks\At21.job
c:\windows\Tasks\At22.job
c:\windows\Tasks\At23.job
c:\windows\Tasks\At24.job
c:\windows\Tasks\At25.job
c:\windows\Tasks\At26.job
c:\windows\Tasks\At27.job
c:\windows\Tasks\At28.job
c:\windows\Tasks\At29.job
c:\windows\Tasks\At3.job
c:\windows\Tasks\At30.job
c:\windows\Tasks\At31.job
c:\windows\Tasks\At32.job
c:\windows\Tasks\At33.job
c:\windows\Tasks\At34.job
c:\windows\Tasks\At35.job
c:\windows\Tasks\At36.job
c:\windows\Tasks\At37.job
c:\windows\Tasks\At38.job
c:\windows\Tasks\At39.job
c:\windows\Tasks\At4.job
c:\windows\Tasks\At40.job
c:\windows\Tasks\At41.job
c:\windows\Tasks\At42.job
c:\windows\Tasks\At43.job
c:\windows\Tasks\At44.job
c:\windows\Tasks\At45.job
c:\windows\Tasks\At46.job
c:\windows\Tasks\At47.job
c:\windows\Tasks\At48.job
c:\windows\Tasks\At49.job
c:\windows\Tasks\At5.job
c:\windows\Tasks\At50.job
c:\windows\Tasks\At51.job
c:\windows\Tasks\At52.job
c:\windows\Tasks\At53.job
c:\windows\Tasks\At54.job
c:\windows\Tasks\At55.job
c:\windows\Tasks\At56.job
c:\windows\Tasks\At57.job
c:\windows\Tasks\At58.job
c:\windows\Tasks\At59.job
c:\windows\Tasks\At6.job
c:\windows\Tasks\At60.job
c:\windows\Tasks\At61.job
c:\windows\Tasks\At62.job
c:\windows\Tasks\At63.job
c:\windows\Tasks\At64.job
c:\windows\Tasks\At65.job
c:\windows\Tasks\At66.job
c:\windows\Tasks\At67.job
c:\windows\Tasks\At68.job
c:\windows\Tasks\At69.job
c:\windows\Tasks\At7.job
c:\windows\Tasks\At70.job
c:\windows\Tasks\At71.job
c:\windows\Tasks\At72.job
c:\windows\Tasks\At73.job
c:\windows\Tasks\At74.job
c:\windows\Tasks\At75.job
c:\windows\Tasks\At76.job
c:\windows\Tasks\At77.job
c:\windows\Tasks\At78.job
c:\windows\Tasks\At79.job
c:\windows\Tasks\At8.job
c:\windows\Tasks\At80.job
c:\windows\Tasks\At81.job
c:\windows\Tasks\At82.job
c:\windows\Tasks\At83.job
c:\windows\Tasks\At84.job
c:\windows\Tasks\At85.job
c:\windows\Tasks\At86.job
c:\windows\Tasks\At87.job
c:\windows\Tasks\At88.job
c:\windows\Tasks\At89.job
c:\windows\Tasks\At9.job
c:\windows\Tasks\At90.job
c:\windows\Tasks\At91.job
c:\windows\Tasks\At92.job
c:\windows\Tasks\At93.job
c:\windows\Tasks\At94.job
c:\windows\Tasks\At95.job
c:\windows\Tasks\At96.job

.
((((((((((((((((((((((((( Files Created from 2010-09-21 to 2010-10-21 )))))))))))))))))))))))))))))))
.

2010-10-21 04:51 . 2010-10-21 04:51 -------- d-----w- c:\documents and settings\LocalService\Application Data\McAfee
2010-10-20 22:48 . 2010-10-20 22:48 388096 ----a-r- c:\documents and settings\MegaeraJ\Application Data\Microsoft\Installer\{45A66726-69BC-466B-A7A4-12FCBA4883D7}\HiJackThis.exe
2010-10-20 22:48 . 2010-10-20 22:48 -------- d-----w- c:\program files\Trend Micro
2010-10-20 21:53 . 2010-10-20 21:53 12872 ----a-w- c:\windows\system32\bootdelete.exe
2010-10-20 21:36 . 2010-10-20 21:36 16968 ----a-w- c:\windows\system32\drivers\hitmanpro35.sys
2010-10-20 21:36 . 2010-10-20 21:36 -------- d-----w- c:\program files\Hitman Pro 3.5
2010-10-20 21:35 . 2010-10-20 21:53 -------- d-----w- c:\documents and settings\All Users\Application Data\Hitman Pro
2010-10-14 01:54 . 2010-09-18 06:53 974848 -c----w- c:\windows\system32\dllcache\mfc42.dll
2010-10-14 01:54 . 2010-09-18 06:53 953856 -c----w- c:\windows\system32\dllcache\mfc40u.dll
2010-10-14 01:54 . 2010-08-23 16:12 617472 -c----w- c:\windows\system32\dllcache\comctl32.dll
2010-10-11 03:54 . 2010-10-11 03:54 -------- d-----w- c:\program files\Common Files\Java
2010-10-11 03:54 . 2010-07-17 09:00 423656 ----a-w- c:\windows\system32\deployJava1.dll
2010-10-11 03:54 . 2010-07-17 09:00 423656 ----a-w- c:\program files\Mozilla Firefox\plugins\npdeployJava1.dll
2010-10-11 03:45 . 2010-10-11 03:45 -------- d-----w- c:\documents and settings\All Users\Application Data\McAfee
2010-10-11 03:45 . 2010-10-11 03:45 -------- d-----w- c:\documents and settings\All Users\Application Data\McAfee Security Scan
2010-10-11 03:45 . 2010-10-21 04:51 -------- d-----w- c:\program files\McAfee Security Scan
2010-10-11 03:42 . 2010-10-21 01:18 16856 ----a-w- c:\program files\Mozilla Firefox\plugin-container.exe
2010-10-11 03:42 . 2010-10-21 01:18 719832 ----a-w- c:\program files\Mozilla Firefox\mozcpp19.dll
2010-10-05 04:43 . 2010-04-29 19:39 38224 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-10-05 04:43 . 2010-04-29 19:39 20952 ----a-w- c:\windows\system32\drivers\mbam.sys
2010-09-21 07:21 . 2010-09-21 07:21 -------- d-----w- c:\documents and settings\MegaeraJ\Application Data\DVDVideoSoftIEHelpers

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"dla"="c:\windows\system32\dla\tfswctrl.exe" [2004-08-13 122939]
"Broadcom Wireless Manager UI"="c:\windows\system32\WLTRAY.exe" [2007-03-16 1392640]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2006-05-01 7561216]
"nwiz"="nwiz.exe" [2006-05-01 1519616]
"NVHotkey"="nvHotkey.dll" [2006-05-01 73728]
"SigmatelSysTrayApp"="c:\program files\SigmaTel\C-Major Audio\WDM\stsystra.exe" [2007-05-10 405504]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2006-03-08 761947]
"ISTray"="c:\program files\Spyware Doctor\pctsTray.exe" [2010-05-27 1287120]

c:\documents and settings\MegaeraJ\Start Menu\Programs\Stuff XP Put Here\Startup\
MagicDisc.lnk - c:\program files\MagicDisc\MagicDisc.exe [2009-3-17 576000]

c:\documents and settings\All Users\Start Menu\Programs\Startup\
McAfee Security Scan Plus.lnk - c:\program files\McAfee Security Scan\2.0.181\SSScheduler.exe [2010-1-15 255536]
TabUserW.exe.lnk - c:\windows\system32\WTablet\TabUserW.exe [2008-8-1 140848]

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-06-20 02:04 35760 ----a-w- c:\program files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\DVDLauncher]
2004-10-12 20:54 57344 ------w- c:\program files\CyberLink\PowerDVD\DVDLauncher.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Google Update]
2008-09-19 07:36 133104 ----atw- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2010-09-24 06:10 421160 ----a-w- c:\program files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-09-08 15:17 421888 ----a-w- c:\program files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\UpdateManager]
2004-01-07 05:01 110592 ----a-w- c:\program files\Common Files\Sonic\Update Manager\sgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"c:\\Program Files\\BitTorrent\\bittorrent.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\manager.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\monitor.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\server.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\support\\bin\\win\\RosettaStoneLtdServices.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\RosettaStoneVersion3.exe"=
"c:\\Program Files\\DNA\\btdna.exe"=
"c:\\Program Files\\AIM6\\aim6.exe"=
"c:\\Softimage\\XSI_5.11\\Application\\bin\\XSI.exe"=
"c:\\Program Files\\Common Files\\Adobe\\CS4ServiceManager\\CS4ServiceManager.exe"=
"c:\\Program Files\\Common Files\\AOL\\Loader\\aolload.exe"=
"c:\\Program Files\\Pando Networks\\Media Booster\\PMB.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"5353:TCP"= 5353:TCP:*:Disabled:Adobe CSI CS4
"57605:TCP"= 57605:TCP:Pando Media Booster
"57605:UDP"= 57605:UDP:Pando Media Booster
"1033:TCP"= 1033:TCP:Akamai NetSession Interface
"5000:UDP"= 5000:UDP:Akamai NetSession Interface

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [8/13/2009 9:57 PM 64288]
R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [4/4/2010 1:28 PM 218592]
R2 Akamai;Akamai NetSession Interface;c:\windows\System32\svchost.exe -k Akamai [8/12/2004 10:06 AM 14336]
R2 Browser Defender Update Service;Browser Defender Update Service;c:\program files\Spyware Doctor\BDT\BDTUpdateService.exe [4/4/2010 1:30 PM 112592]
R2 sdAuxService;PC Tools Auxiliary Service;c:\program files\Spyware Doctor\pctsAuxs.exe [4/4/2010 1:28 PM 366840]
R2 TabletServicePen;TabletServicePen;c:\windows\system32\Pen_Tablet.exe [6/3/2010 1:25 PM 2749736]
R2 Viewpoint Manager Service;Viewpoint Manager Service;c:\program files\Viewpoint\Common\ViewpointService.exe [5/11/2009 9:02 PM 24652]
R2 WTouchService;WTouch Service;c:\program files\WTouch\WTouchService.exe [6/3/2010 1:26 PM 113448]
S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [2/4/2010 11:52 AM 1352832]
S3 McComponentHostService;McAfee Security Scan Component Host Service;c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe [1/15/2010 8:49 AM 227232]
S3 wacmoumonitor;Wacom Mode Helper;c:\windows\system32\drivers\wacmoumonitor.sys [6/3/2010 1:25 PM 15656]
S3 XDva320;XDva320;\??\c:\windows\system32\XDva320.sys --> c:\windows\system32\XDva320.sys [?]
S4 sptd;sptd;c:\windows\system32\drivers\sptd.sys [3/17/2009 7:26 PM 717296]

--- Other Services/Drivers In Memory ---

*Deregistered* - PCTSDInjDriver32

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
Akamai REG_MULTI_SZ Akamai
.
Contents of the 'Scheduled Tasks' folder

2010-10-14 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2010-02-04 01:03]

2010-10-03 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 16:34]

2010-10-20 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004Core.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]

2010-10-21 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004UA.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]
.
.
------- Supplementary Scan -------
.
IE: &AIM Toolbar Search - c:\documents and settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~3\Office10\EXCEL.EXE/3000
IE: Free YouTube Download - c:\documents and settings\MegaeraJ\Application Data\DVDVideoSoftIEHelpers\youtubedownload.htm
FF - ProfilePath - c:\documents and settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\
FF - prefs.js: browser.search.defaulturl - hxxp://slirsredirect.search.aol.com/slirs_http/sredir?sredir=2706&invocationType=tb50fftrie7&query=
FF - prefs.js: browser.search.selectedEngine - Google
FF - prefs.js: browser.startup.homepage - hxxp://www.deviantart.com/
FF - prefs.js: keyword.URL - hxxp://search.newtabking.com/?t=1&q=
FF - plugin: c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\1.2.183.39\npGoogleOneClick8.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nppl3260.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\npqtplugin.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nprpjplug.dll
FF - plugin: c:\program files\Java\jre6\bin\new_plugin\npdeployJava1.dll
FF - plugin: c:\program files\Mozilla Firefox\plugins\npbittorrent.dll
FF - plugin: c:\program files\Pando Networks\Media Booster\npPandoWebPlugin.dll
FF - plugin: c:\program files\TabletPlugins\npwacom.dll
FF - plugin: c:\program files\Viewpoint\Viewpoint Media Player\npViewpoint.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbaam7a8h", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqz9s", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqs8s", true); // Simplified
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--j6w193g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4ar", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4a87g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7c0a67fbc", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7cvafr", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kpry57d", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kprw13d", true); // Simplified
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.ipc.plugins.enabled", false);
.
- - - - ORPHANS REMOVED - - - -

URLSearchHooks-HookURL - (no file)
URLSearchHooks-Rank - (no file)
HKCU-Run-Aim6 - (no file)


Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe catchme.sys CLASSPNP.SYS disk.sys PCTCore.sys ACPI.sys hal.dll >>UNKNOWN [0x866EE446]<<
kernel: MBR read successfully
detected MBR rootkit hooks:
\Driver\Disk -> CLASSPNP.SYS @ 0xf7675f28
\Driver\ACPI -> ACPI.sys @ 0xf74e8cb8
\Driver\atapi -> atapi.sys @ 0xf7480852
IoDeviceObjectType -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
\Device\Harddisk0\DR0 -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
NDIS: Dell Wireless 1390 WLAN Mini-Card -> SendCompleteHandler -> NDIS.sys @ 0xf735ebb0
PacketIndicateHandler -> NDIS.sys @ 0xf736ba21
SendHandler -> NDIS.sys @ 0xf734987b
user & kernel MBR OK

**************************************************************************
.
Completion time: 2010-10-21 02:32:54
ComboFix-quarantined-files.txt 2010-10-21 06:32

Pre-Run: 92,861,009,920 bytes free
Post-Run: 92,981,321,728 bytes free

WindowsXP-KB310994-SP2-Home-BootDisk-ENU.exe
[boot loader]
timeout=2
default=multi(0)disk(0)rdisk(0)partition(1)\WINDOWS
[operating systems]
c:\cmdcons\BOOTSECT.DAT="Microsoft Windows Recovery Console" /cmdcons
UnsupportedDebug="do not select this" /debug
multi(0)disk(0)rdisk(0)partition(1)\WINDOWS="Microsoft Windows XP Home Edition" /noexecute=optin /fastdetect

- - End Of File - - 5979E5F1E4F67A0DA454357D5E6EE3AB
 
This one didn't fit in the last post.

Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 2:43:01 AM, on 10/21/2010
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP3 (6.00.2900.5512)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\csrss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\WTouch\WTouchService.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\bcmwltry.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\Program Files\Spyware Doctor\BDT\BDTUpdateService.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\Program Files\Super_DVD_Creator_9.8\NMSAccessU.exe
C:\WINDOWS\system32\nvsvc32.exe
C:\Program Files\Spyware Doctor\pctsAuxs.exe
C:\Program Files\Spyware Doctor\pctsSvc.exe
C:\WINDOWS\system32\Tablet.exe
C:\WINDOWS\system32\Pen_Tablet.exe
C:\Program Files\Viewpoint\Common\ViewpointService.exe
C:\Program Files\WTouch\WTouchUser.exe
C:\WINDOWS\System32\alg.exe
C:\WINDOWS\system32\Tablet.exe
C:\Program Files\Spyware Doctor\pctsTray.exe
C:\WINDOWS\explorer.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Trend Micro\HiJackThis\HiJackThis.exe
C:\WINDOWS\system32\wbem\wmiprvse.exe

R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: Browser Defender BHO - {2A0F3D1B-0909-4FF4-B272-609CCE6054E7} - C:\Program Files\Spyware Doctor\BDT\PCTBrowserDefender.dll
O2 - BHO: Spybot-S&D IE Protection - {53707962-6F74-2D53-2644-206D7942484F} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O2 - BHO: AOL Search Enhancement - {54EB34EA-E6BE-4CFD-9F4F-C4A0C2EAFA22} - C:\Program Files\AIM Search\AOLSearch.dll
O2 - BHO: DriveLetterAccess - {5CA3D70E-1895-11CF-8E15-001234567890} - C:\WINDOWS\system32\dla\tfswshx.dll
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: PC Tools Browser Guard - {472734EA-242A-422B-ADF8-83D1E48CC825} - C:\Program Files\Spyware Doctor\BDT\PCTBrowserDefender.dll
O4 - HKLM\..\Run: [dla] C:\WINDOWS\system32\dla\tfswctrl.exe
O4 - HKLM\..\Run: [Broadcom Wireless Manager UI] C:\WINDOWS\system32\WLTRAY.exe
O4 - HKLM\..\Run: [NvCplDaemon] RUNDLL32.EXE C:\WINDOWS\system32\NvCpl.dll,NvStartup
O4 - HKLM\..\Run: [nwiz] nwiz.exe /installquiet
O4 - HKLM\..\Run: [NVHotkey] rundll32.exe nvHotkey.dll,Start
O4 - HKLM\..\Run: [SigmatelSysTrayApp] %ProgramFiles%\SigmaTel\C-Major Audio\WDM\stsystra.exe
O4 - HKLM\..\Run: [SynTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
O4 - HKLM\..\Run: [ISTray] "C:\Program Files\Spyware Doctor\pctsTray.exe"
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - Startup: MagicDisc.lnk = C:\Program Files\MagicDisc\MagicDisc.exe
O4 - Global Startup: McAfee Security Scan Plus.lnk = ?
O4 - Global Startup: TabUserW.exe.lnk = C:\WINDOWS\system32\WTablet\TabUserW.exe
O8 - Extra context menu item: &AIM Toolbar Search - C:\Documents and Settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~3\Office10\EXCEL.EXE/3000
O8 - Extra context menu item: Free YouTube Download - C:\Documents and Settings\MegaeraJ\Application Data\DVDVideoSoftIEHelpers\youtubedownload.htm
O9 - Extra button: AIM Toolbar - {0b83c99c-1efa-4259-858f-bcb33e007a5b} - C:\Program Files\AIM Toolbar\aimtb.dll (file missing)
O9 - Extra button: (no name) - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra 'Tools' menuitem: Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
O23 - Service: Autodesk Licensing Service - Autodesk - C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: Browser Defender Update Service - Unknown owner - C:\Program Files\Spyware Doctor\BDT\BDTUpdateService.exe
O23 - Service: FLEXnet Licensing Service - Acresso Software Inc. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: Lavasoft Ad-Aware Service - Lavasoft - C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe
O23 - Service: McAfee Security Scan Component Host Service (McComponentHostService) - McAfee, Inc. - C:\Program Files\McAfee Security Scan\2.0.181\McCHSvc.exe
O23 - Service: mental ray 3.5 Satellite (32-bit) (mi-raysat_3dsmax9_32) - Unknown owner - C:\Program Files\Autodesk\3ds Max 9\mentalray\satellite\raysat_3dsmax9_32server.exe
O23 - Service: NMSAccessU - Unknown owner - C:\Program Files\Super_DVD_Creator_9.8\NMSAccessU.exe
O23 - Service: NVIDIA Display Driver Service (NVSvc) - NVIDIA Corporation - C:\WINDOWS\system32\nvsvc32.exe
O23 - Service: RaySat3_4_6_18 Server (RaySat3_4_6_18Server) - Unknown owner - C:\Softimage\XSI_5.11\Application\bin\raysat3_4_6_18server.exe
O23 - Service: PC Tools Auxiliary Service (sdAuxService) - PC Tools - C:\Program Files\Spyware Doctor\pctsAuxs.exe
O23 - Service: PC Tools Security Service (sdCoreService) - PC Tools - C:\Program Files\Spyware Doctor\pctsSvc.exe
O23 - Service: SPM License Server (spmd) - Unknown owner - C:\WINDOWS\system32\spm\spmd.exe (file missing)
O23 - Service: TabletService - Wacom Technology, Corp. - C:\WINDOWS\system32\Tablet.exe
O23 - Service: TabletServicePen - Wacom Technology, Corp. - C:\WINDOWS\system32\Pen_Tablet.exe
O23 - Service: Viewpoint Manager Service - Viewpoint Corporation - C:\Program Files\Viewpoint\Common\ViewpointService.exe
O23 - Service: Dell Wireless WLAN Tray Service (wltrysvc) - Unknown owner - C:\WINDOWS\System32\WLTRYSVC.EXE
O23 - Service: WTouch Service (WTouchService) - Wacom Technology, Corp. - C:\Program Files\WTouch\WTouchService.exe

--
End of file - 8113 bytes


You are a brave soldier for making it to the end. Thank You. :)
 
Mcafee security scan most likely got installed when you did adobe or Java. There was an option to uncheck it before you downloaded it.


Please uninstall the following entries in add/remove programs along with any non genuine programs you have installed, if any. I noticed you had bittorrent entry in hijackthis.

McAfee Security Scan Plus
Uninstall 1.0.0.1
Viewpoint Media Player

Also please disable all addon's in firefox for the time being and see if the redirects stop.

1. Go to Start > Run > type Notepad.exe and click OK to open Notepad.
It must be Notepad, not Wordpad.
2. Copy the text in the below code box

Code:
File::
c:\windows\system32\XDva320.sys 

Driver::
XDva320

3. Go to the Notepad window and click Edit > Paste
4. Then click File > Save
5. Name the file CFScript.txt - Save the file to your Desktop
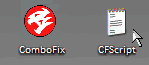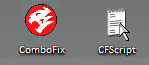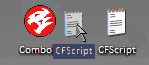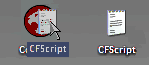
6. Then drag the CFScript (hold the left mouse button while dragging the file) and drop it (release the left mouse button) into ComboFix.exe as you see in the screenshot below. Important: Perform this instruction carefully!


CFScript-1.gif


ComboFix will begin to execute, just follow the prompts.
After reboot (in case it asks to reboot), it will produce a log for you.
Post that log (Combofix.txt) in your next reply.

After this, we will have to work on your possible MBR infection. I'm off to work again so i will post again later tonight after reviewing your logs.
 
Hello,

After disabling the Firefox add-ons, the redirecting and random tab pop-ups still persist. The redirects are far less frequent. They used to be every link, now they seem to only happen consistently to the first link I click on and then stop.

Here is the new ComboFix Log:

ComboFix 10-10-20.04 - MegaeraJ 10/21/2010 14:31:56.2.2 - x86
Running from: c:\documents and settings\MegaeraJ\Desktop\ComboFix.exe
Command switches used :: c:\documents and settings\MegaeraJ\Desktop\CFScript.txt

FILE ::
"c:\windows\system32\XDva320.sys"
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.

-------\Legacy_XDVA320
-------\Service_XDva320


((((((((((((((((((((((((( Files Created from 2010-09-21 to 2010-10-21 )))))))))))))))))))))))))))))))
.

No new files created in this timespan

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"dla"="c:\windows\system32\dla\tfswctrl.exe" [2004-08-13 122939]
"Broadcom Wireless Manager UI"="c:\windows\system32\WLTRAY.exe" [2007-03-16 1392640]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2006-05-01 7561216]
"nwiz"="nwiz.exe" [2006-05-01 1519616]
"NVHotkey"="nvHotkey.dll" [2006-05-01 73728]
"SigmatelSysTrayApp"="c:\program files\SigmaTel\C-Major Audio\WDM\stsystra.exe" [2007-05-10 405504]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2006-03-08 761947]
"ISTray"="c:\program files\Spyware Doctor\pctsTray.exe" [2010-05-27 1287120]

c:\documents and settings\MegaeraJ\Start Menu\Programs\Stuff XP Put Here\Startup\
MagicDisc.lnk - c:\program files\MagicDisc\MagicDisc.exe [2009-3-17 576000]

c:\documents and settings\All Users\Start Menu\Programs\Startup\
TabUserW.exe.lnk - c:\windows\system32\WTablet\TabUserW.exe [2008-8-1 140848]

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-06-20 02:04 35760 ----a-w- c:\program files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\DVDLauncher]
2004-10-12 20:54 57344 ------w- c:\program files\CyberLink\PowerDVD\DVDLauncher.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Google Update]
2008-09-19 07:36 133104 ----atw- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2010-09-24 06:10 421160 ----a-w- c:\program files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-09-08 15:17 421888 ----a-w- c:\program files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\UpdateManager]
2004-01-07 05:01 110592 ----a-w- c:\program files\Common Files\Sonic\Update Manager\sgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\manager.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\monitor.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\server.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\support\\bin\\win\\RosettaStoneLtdServices.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\RosettaStoneVersion3.exe"=
"c:\\Program Files\\DNA\\btdna.exe"=
"c:\\Program Files\\AIM6\\aim6.exe"=
"c:\\Softimage\\XSI_5.11\\Application\\bin\\XSI.exe"=
"c:\\Program Files\\Common Files\\Adobe\\CS4ServiceManager\\CS4ServiceManager.exe"=
"c:\\Program Files\\Common Files\\AOL\\Loader\\aolload.exe"=
"c:\\Program Files\\Pando Networks\\Media Booster\\PMB.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"5353:TCP"= 5353:TCP:*:Disabled:Adobe CSI CS4
"57605:TCP"= 57605:TCP:Pando Media Booster
"57605:UDP"= 57605:UDP:Pando Media Booster
"1039:TCP"= 1039:TCP:Akamai NetSession Interface
"5000:UDP"= 5000:UDP:Akamai NetSession Interface

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [8/13/2009 9:57 PM 64288]
R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [4/4/2010 1:28 PM 218592]
R2 Akamai;Akamai NetSession Interface;c:\windows\System32\svchost.exe -k Akamai [8/12/2004 10:06 AM 14336]
R2 Browser Defender Update Service;Browser Defender Update Service;c:\program files\Spyware Doctor\BDT\BDTUpdateService.exe [4/4/2010 1:30 PM 112592]
R2 sdAuxService;PC Tools Auxiliary Service;c:\program files\Spyware Doctor\pctsAuxs.exe [4/4/2010 1:28 PM 366840]
R2 TabletServicePen;TabletServicePen;c:\windows\system32\Pen_Tablet.exe [6/3/2010 1:25 PM 2749736]
R2 WTouchService;WTouch Service;c:\program files\WTouch\WTouchService.exe [6/3/2010 1:26 PM 113448]
S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [2/4/2010 11:52 AM 1352832]
S3 McComponentHostService;McAfee Security Scan Component Host Service;"c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe" --> c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe [?]
S3 wacmoumonitor;Wacom Mode Helper;c:\windows\system32\drivers\wacmoumonitor.sys [6/3/2010 1:25 PM 15656]
S4 sptd;sptd;c:\windows\system32\drivers\sptd.sys [3/17/2009 7:26 PM 717296]

--- Other Services/Drivers In Memory ---

*Deregistered* - PCTSDInjDriver32

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
Akamai REG_MULTI_SZ Akamai
.
Contents of the 'Scheduled Tasks' folder

2010-10-14 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2010-02-04 01:03]

2010-10-03 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 16:34]

2010-10-20 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004Core.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]

2010-10-21 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004UA.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]
.
.
------- Supplementary Scan -------
.
IE: &AIM Toolbar Search - c:\documents and settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~3\Office10\EXCEL.EXE/3000
IE: Free YouTube Download
FF - ProfilePath - c:\documents and settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\
FF - prefs.js: browser.search.defaulturl - hxxp://slirsredirect.search.aol.com/slirs_http/sredir?sredir=2706&invocationType=tb50fftrie7&query=
FF - prefs.js: browser.search.selectedEngine - Google
FF - prefs.js: browser.startup.homepage - hxxp://www.deviantart.com/
FF - prefs.js: keyword.URL - hxxp://search.newtabking.com/?t=1&q=
FF - plugin: c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\1.2.183.39\npGoogleOneClick8.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nppl3260.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\npqtplugin.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nprpjplug.dll
FF - plugin: c:\program files\Java\jre6\bin\new_plugin\npdeployJava1.dll
FF - plugin: c:\program files\Pando Networks\Media Booster\npPandoWebPlugin.dll
FF - plugin: c:\program files\TabletPlugins\npwacom.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbaam7a8h", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqz9s", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqs8s", true); // Simplified
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--j6w193g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4ar", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4a87g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7c0a67fbc", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7cvafr", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kpry57d", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kprw13d", true); // Simplified
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.ipc.plugins.enabled", false);
.
- - - - ORPHANS REMOVED - - - -

URLSearchHooks-HookURL - (no file)
URLSearchHooks-Rank - (no file)


Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe CLASSPNP.SYS disk.sys PCTCore.sys ACPI.sys hal.dll >>UNKNOWN [0x86734446]<<
kernel: MBR read successfully
detected MBR rootkit hooks:
\Driver\Disk -> CLASSPNP.SYS @ 0xf7675f28
\Driver\ACPI -> ACPI.sys @ 0xf74e8cb8
\Driver\atapi -> atapi.sys @ 0xf7480852
IoDeviceObjectType -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
\Device\Harddisk0\DR0 -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
NDIS: Dell Wireless 1390 WLAN Mini-Card -> SendCompleteHandler -> NDIS.sys @ 0xf735ebb0
PacketIndicateHandler -> NDIS.sys @ 0xf734da0d
SendHandler -> NDIS.sys @ 0xf7361b40
user & kernel MBR OK

**************************************************************************
.
--------------------- DLLs Loaded Under Running Processes ---------------------

- - - - - - - > 'explorer.exe'(2780)
c:\program files\Spyware Doctor\pctgmhk.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
c:\program files\Common Files\Adobe\Adobe Drive CS4\AdobeDriveCS4_NP.dll
.
------------------------ Other Running Processes ------------------------
.
c:\windows\System32\WLTRYSVC.EXE
c:\windows\System32\bcmwltry.exe
c:\program files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files\Common Files\Autodesk Shared\Service\AdskScSrv.exe
c:\program files\Bonjour\mDNSResponder.exe
c:\program files\Java\jre6\bin\jqs.exe
c:\program files\Autodesk\3ds Max 9\mentalray\satellite\raysat_3dsmax9_32server.exe
c:\program files\Super_DVD_Creator_9.8\NMSAccessU.exe
c:\windows\system32\nvsvc32.exe
c:\softimage\XSI_5.11\Application\bin\raysat3_4_6_18server.exe
c:\program files\Spyware Doctor\pctsSvc.exe
c:\windows\system32\Tablet.exe
c:\program files\WTouch\WTouchUser.exe
c:\windows\system32\rundll32.exe
c:\windows\system32\Tablet.exe
.
**************************************************************************
.
Completion time: 2010-10-21 15:06:31 - machine was rebooted
ComboFix-quarantined-files.txt 2010-10-21 19:06
ComboFix2.txt 2010-10-21 06:32

Pre-Run: 93,036,728,320 bytes free
Post-Run: 92,976,201,728 bytes free

- - End Of File - - 5E426AEDED274E928B6ABD56898AE50C


Thank You! :)
 
Download and run mbr.exe Save it to your desktop and double click on it. There will be a black box appear and quickly disappear. A log will be created on your desktop called mbr as a notepad file. Please copy and paste whats inside the log back here.
 
And here is the SUPERAntiSpyware log file:

SUPERAntiSpyware Scan Log
http://www.superantispyware.com

Generated 10/22/2010 at 00:39 AM

Application Version : 4.44.1000

Core Rules Database Version : 5732
Trace Rules Database Version: 3544

Scan type : Quick Scan
Total Scan Time : 00:17:15

Memory items scanned : 467
Memory threats detected : 0
Registry items scanned : 1648
Registry threats detected : 0
File items scanned : 6943
File threats detected : 208

Adware.Tracking Cookie
C:\Documents and Settings\MegaeraJ\Cookies\[email protected][2].txt
media1.break.com [ C:\Documents and Settings\LocalService\Application Data\Macromedia\Flash Player\#SharedObjects\GQXGGX8C ]
acvs.mediaonenetwork.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
broadcast.piximedia.fr [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
cache.specificmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
cdn.eyewonder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
cdn.insights.gravity.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
cdn1.eyewonder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
cdn4.specificclick.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
content.oddcast.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
convoad.technoratimedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
countdownpage.createyourcountdown.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
crackle.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
hs.interpolls.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
i.adultswim.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
ia.media-imdb.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
ictv-cdn-hw.indieclicktv.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
ictv-ic-ec.indieclicktv.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
imgs.adverticum.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
indieclick.3janecdn.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
interclick.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
m1.2mdn.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
macromedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.avclub.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.entertonement.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.jambocast.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.kvue.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.mtvnservices.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.resulthost.org [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.scanscout.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media.tattomedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
media1.break.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
mediaforgews.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
memecounter.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
msnbcmedia.msn.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
objects.tremormedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
oddcast.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
piximedia.fr [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
s0.2mdn.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
secure-us.imrworldwide.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
sex.healthguru.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
sftrack.searchforce.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
static.2mdn.net [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
www.adultswim.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
www.crackle.com [ C:\Documents and Settings\MegaeraJ\Application Data\Macromedia\Flash Player\#SharedObjects\WSDSWFPE ]
.specificmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.imrworldwide.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.eyewonder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
adserver.mmoguru.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.game-advertising-online.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.specificmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
dc.tremormedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.kanoodle.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.eyewonder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.legolas-media.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.adxpose.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.legolas-media.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.bizrate.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.2mdn.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
optimize.indieclick.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.edgeadx.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.media.photobucket.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.edgeadx.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.qsstats.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.mediafire.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
fidelity.rotator.hadj7.adjuggler.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
adserver.adpredictive.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.amex-insights.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.mediabrandsww.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.burstnetads.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
y.d.j.cltomedia.info [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.cltomedia.info [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
cltomedia.info [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.zanox.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.77tracking.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.ontoplist.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.adcentriconline.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.sothinkmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.legolas-media.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.thefind.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
gejc4dhq0s.s.ad6media.fr [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.clickintext.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.himedia.individuad.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.naturalmediasolutions.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.naturalmediasolutions.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.cracked.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
clickbangpop.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
d.mediadakine.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.clickfuse.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.technoratimedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.media.adfrontiers.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.lucidmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
ext-us.bestofmedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.legolas-media.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.kanoodle.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
optimize.indieclick.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.trackimizer.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
n-traffic.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.invitemedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.collective-media.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.invitemedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.advertise.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.bizzclick.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.media6degrees.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
advert.funimation.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.pointroll.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.intermundomedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.chitika.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
bridge1.admarketplace.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.admarketplace.net [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.apartmentfinder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.apartmentfinder.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
www.icityfind.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.invitemedia.com [ C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\cookies.sqlite ]
.imrworldwide.com [ C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Chrome\User Data\Default\Cookies ]
media.mtvnservices.com [ C:\Documents and Settings\NetworkService\Application Data\Macromedia\Flash Player\#SharedObjects\52AAU2LP ]
media.scanscout.com [ C:\Documents and Settings\NetworkService\Application Data\Macromedia\Flash Player\#SharedObjects\52AAU2LP ]
media1.break.com [ C:\Documents and Settings\NetworkService\Application Data\Macromedia\Flash Player\#SharedObjects\52AAU2LP ]
objects.tremormedia.com [ C:\Documents and Settings\NetworkService\Application Data\Macromedia\Flash Player\#SharedObjects\52AAU2LP ]
secure-us.imrworldwide.com [ C:\Documents and Settings\NetworkService\Application Data\Macromedia\Flash Player\#SharedObjects\52AAU2LP ]

Trojan.Agent/Gen
C:\DOCUMENTS AND SETTINGS\MEGAERAJ\DESKTOP\85T7W9K3.EXE
 
I did notice that you had it installed so download and run Ccleaner. Just open the program and click on run cleaner. This will clean out all your old temp intenet and system files.

http://download.cnet.com/ccleaner/

Did you uninstall those programs I listed? Again, if you have any non-genuine or illegal software installed please uninstall it. It's very important to let users know that a lot of non genuine/illegal software comes bundled with malware.

Also I would like to see another combofix log to see if it still detects a possible mbr infection. Please download the latest combofix from here and run it and post its log along with a fresh hijackthis log.

http://download.bleepingcomputer.com/sUBs/ComboFix.exe
 
Hello,

I did uninstall everything you mentioned plus a couple of other things (hopefully I didn't miss anything.) I used the add/remove feature from the Control Panel. Should I also be going through my hard drive files to see if there is anything leftover from the uninstalls?

When I ran ComboFix this time, it didn't give me any message about detecting anything or having to reboot. However, after the scan it took an unusually long time to shut down and it never opened up the log. After about an hour of waiting, I restarted the computer and retrieved the log.

The redirects are back to full force. There is also an error message about a Generic Host Process failure and the task bar seems to randomly switch to the classic version every once in a while (mostly following the error message.)

I apologize if this is proving to be an unusually pesky problem and I greatly appreciate all of the help you have given me thus far.

And lastly here is that ComboFix log:

ComboFix 10-10-22.03 - MegaeraJ 10/22/2010 18:44:31.3.2 - x86
Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.1022.598 [GMT -4:00]
Running from: C:\Documents and Settings\MegaeraJ\Desktop\ComboFix.exe
.

((((((((((((((((((((((((( Files Created from 2010-09-22 to 2010-10-22 )))))))))))))))))))))))))))))))
.

2010-10-22 22:32:21 . 2010-10-22 22:32:24 -------- d-----w- C:\Program Files\CCleaner
2010-10-22 04:19:29 . 2010-10-22 04:19:29 -------- d-----w- C:\Documents and Settings\MegaeraJ\Application Data\SUPERAntiSpyware.com
2010-10-22 04:19:29 . 2010-10-22 04:19:29 -------- d-----w- C:\Documents and Settings\All Users\Application Data\SUPERAntiSpyware.com
2010-10-22 04:19:18 . 2010-10-22 04:19:35 -------- d-----w- C:\Program Files\SUPERAntiSpyware
2010-10-21 19:06:09 . 2010-10-21 19:06:09 -------- d-s---w- C:\Documents and Settings\NetworkService\UserData
2010-10-21 04:51:53 . 2010-10-21 04:51:53 -------- d-----w- C:\Documents and Settings\LocalService\Application Data\McAfee
2010-10-20 22:48:13 . 2010-10-20 22:48:13 388096 ----a-r- C:\Documents and Settings\MegaeraJ\Application Data\Microsoft\Installer\{45A66726-69BC-466B-A7A4-12FCBA4883D7}\HiJackThis.exe
2010-10-20 22:48:11 . 2010-10-20 22:48:11 -------- d-----w- C:\Program Files\Trend Micro
2010-10-20 21:53:30 . 2010-10-20 21:53:32 12872 ----a-w- C:\WINDOWS\system32\bootdelete.exe
2010-10-20 21:36:08 . 2010-10-20 21:36:08 16968 ----a-w- C:\WINDOWS\system32\drivers\hitmanpro35.sys
2010-10-20 21:36:05 . 2010-10-20 21:36:05 -------- d-----w- C:\Program Files\Hitman Pro 3.5
2010-10-20 21:35:28 . 2010-10-20 21:53:16 -------- d-----w- C:\Documents and Settings\All Users\Application Data\Hitman Pro
2010-10-14 01:54:47 . 2010-09-18 06:53:25 974848 -c----w- C:\WINDOWS\system32\dllcache\mfc42.dll
2010-10-14 01:54:47 . 2010-09-18 06:53:25 953856 -c----w- C:\WINDOWS\system32\dllcache\mfc40u.dll
2010-10-14 01:54:28 . 2010-08-23 16:12:04 617472 -c----w- C:\WINDOWS\system32\dllcache\comctl32.dll
2010-10-11 03:54:55 . 2010-10-11 03:54:55 -------- d-----w- C:\Program Files\Common Files\Java
2010-10-11 03:54:39 . 2010-07-17 09:00:04 423656 ----a-w- C:\WINDOWS\system32\deployJava1.dll
2010-10-11 03:54:39 . 2010-07-17 09:00:04 423656 ----a-w- C:\Program Files\Mozilla Firefox\plugins\npdeployJava1.dll
2010-10-11 03:45:45 . 2010-10-11 03:45:45 -------- d-----w- C:\Documents and Settings\All Users\Application Data\McAfee
2010-10-11 03:42:34 . 2010-10-21 01:18:47 16856 ----a-w- C:\Program Files\Mozilla Firefox\plugin-container.exe
2010-10-11 03:42:30 . 2010-10-21 01:18:45 719832 ----a-w- C:\Program Files\Mozilla Firefox\mozcpp19.dll
2010-10-05 04:43:25 . 2010-04-29 19:39:38 38224 ----a-w- C:\WINDOWS\system32\drivers\mbamswissarmy.sys
2010-10-05 04:43:23 . 2010-04-29 19:39:26 20952 ----a-w- C:\WINDOWS\system32\drivers\mbam.sys

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-09-18 16:23:26 . 2004-08-12 13:59:44 974848 ----a-w- C:\WINDOWS\system32\mfc42u.dll
2010-09-18 06:53:25 . 2004-08-12 13:59:44 974848 ----a-w- C:\WINDOWS\system32\mfc42.dll
2010-09-18 06:53:25 . 2004-08-12 13:59:43 954368 ----a-w- C:\WINDOWS\system32\mfc40.dll
2010-09-18 06:53:25 . 2004-08-12 13:59:43 953856 ----a-w- C:\WINDOWS\system32\mfc40u.dll
2010-09-09 14:16:31 . 2004-08-12 14:09:30 667136 ----a-w- C:\WINDOWS\system32\wininet.dll
2010-09-09 14:16:30 . 2004-08-12 14:07:11 61952 ----a-w- C:\WINDOWS\system32\tdc.ocx
2010-09-09 14:16:29 . 2004-08-12 13:58:00 81920 ----a-w- C:\WINDOWS\system32\ieencode.dll
2010-09-08 16:49:49 . 2004-08-12 13:57:51 369664 ----a-w- C:\WINDOWS\system32\html.iec
2010-09-08 15:17:46 . 2010-09-08 15:17:46 94208 ----a-w- C:\WINDOWS\system32\QuickTimeVR.qtx
2010-09-08 15:17:46 . 2010-09-08 15:17:46 69632 ----a-w- C:\WINDOWS\system32\QuickTime.qts
2010-09-01 11:51:14 . 2004-08-12 13:55:52 285824 ----a-w- C:\WINDOWS\system32\atmfd.dll
2010-08-31 13:42:52 . 2004-08-12 14:09:18 1852800 ----a-w- C:\WINDOWS\system32\win32k.sys
2010-08-27 08:02:29 . 2004-08-12 14:07:02 119808 ----a-w- C:\WINDOWS\system32\t2embed.dll
2010-08-27 05:57:43 . 2004-08-12 14:06:30 99840 ----a-w- C:\WINDOWS\system32\srvsvc.dll
2010-08-26 13:39:50 . 2004-08-12 14:06:30 357248 ----a-w- C:\WINDOWS\system32\drivers\srv.sys
2010-08-26 12:52:45 . 2009-04-16 00:21:18 5120 ----a-w- C:\WINDOWS\system32\xpsp4res.dll
2010-08-23 16:12:04 . 2004-08-12 13:56:07 617472 ----a-w- C:\WINDOWS\system32\comctl32.dll
2010-08-17 13:17:06 . 2004-08-12 14:06:19 58880 ----a-w- C:\WINDOWS\system32\spoolsv.exe
2010-08-16 08:45:00 . 2004-08-12 14:04:26 590848 ----a-w- C:\WINDOWS\system32\rpcrt4.dll
2010-08-05 22:32:46 . 2010-08-05 22:32:46 967 ----a-w- C:\WINDOWS\ScUnin.pif
2010-08-05 22:32:46 . 2010-08-05 22:32:46 68096 ----a-w- C:\WINDOWS\ScUnin.exe
2010-07-29 00:59:41 . 2010-07-29 00:54:28 702961740 ----a-w- C:\Program Files\Setup_Atlantica_Lite21410.exe
2010-07-27 22:44:10 . 2010-07-27 22:44:10 91424 ----a-w- C:\WINDOWS\system32\dnssd.dll
2010-07-27 22:44:10 . 2010-07-27 22:44:10 107808 ----a-w- C:\WINDOWS\system32\dns-sd.exe
2010-04-15 22:30:03 . 2010-04-15 22:23:12 940197287 ----a-w- C:\Program Files\FEZsetup_2010-04-01.exe
.

((((((((((((((((((((((((((((( SnapShot@2010-10-21_06.27.12 )))))))))))))))))))))))))))))))))))))))))
.
+ 2010-10-22 04:43:28 . 2010-10-22 04:43:28 16384 C:\WINDOWS\Temp\Perflib_Perfdata_9c.dat
+ 2010-10-22 04:43:23 . 2010-10-22 04:43:23 16384 C:\WINDOWS\Temp\Perflib_Perfdata_760.dat
+ 2010-10-22 04:43:22 . 2010-10-22 04:43:22 16384 C:\WINDOWS\Temp\Perflib_Perfdata_6ac.dat
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 20:07:20 2260480]
"SUPERAntiSpyware"="C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe" [2010-09-28 14:04:57 2424560]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"dla"="C:\WINDOWS\system32\dla\tfswctrl.exe" [2004-08-13 05:05:00 122939]
"Broadcom Wireless Manager UI"="C:\WINDOWS\system32\WLTRAY.exe" [2007-03-16 22:10:54 1392640]
"NvCplDaemon"="C:\WINDOWS\system32\NvCpl.dll" [2006-05-01 19:46:00 7561216]
"nwiz"="nwiz.exe" [2006-05-01 19:46:00 1519616]
"NVHotkey"="nvHotkey.dll" [2006-05-01 19:46:00 73728]
"SigmatelSysTrayApp"="C:\Program Files\SigmaTel\C-Major Audio\WDM\stsystra.exe" [2007-05-10 14:22:32 405504]
"SynTPEnh"="C:\Program Files\Synaptics\SynTP\SynTPEnh.exe" [2006-03-08 16:48:02 761947]
"ISTray"="C:\Program Files\Spyware Doctor\pctsTray.exe" [2010-05-27 20:16:57 1287120]

C:\Documents and Settings\MegaeraJ\Start Menu\Programs\Stuff XP Put Here\Startup\
MagicDisc.lnk - C:\Program Files\MagicDisc\MagicDisc.exe [2009-3-17 576000]

C:\Documents and Settings\All Users\Start Menu\Programs\Startup\
TabUserW.exe.lnk - C:\WINDOWS\system32\WTablet\TabUserW.exe [2008-8-1 140848]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "C:\Program Files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 17:13:36 77824]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2009-09-03 22:21:41 548352 ----a-w- C:\Program Files\SUPERAntiSpyware\SASWINLO.DLL

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-06-20 02:04:47 35760 ----a-w- C:\Program Files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\DVDLauncher]
2004-10-12 20:54:30 57344 ------w- C:\Program Files\CyberLink\PowerDVD\DVDLauncher.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Google Update]
2008-09-19 07:36:00 133104 ----atw- C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2010-09-24 06:10:52 421160 ----a-w- C:\Program Files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-09-08 15:17:42 421888 ----a-w- C:\Program Files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\UpdateManager]
2004-01-07 05:01:00 110592 ----a-w- C:\Program Files\Common Files\Sonic\Update Manager\sgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"C:\\Program Files\\Autodesk\\Backburner\\manager.exe"=
"C:\\Program Files\\Autodesk\\Backburner\\monitor.exe"=
"C:\\Program Files\\Autodesk\\Backburner\\server.exe"=
"C:\\Program Files\\Messenger\\msmsgs.exe"=
"C:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\support\\bin\\win\\RosettaStoneLtdServices.exe"=
"C:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\RosettaStoneVersion3.exe"=
"C:\\Program Files\\DNA\\btdna.exe"=
"C:\\Program Files\\AIM6\\aim6.exe"=
"C:\\Softimage\\XSI_5.11\\Application\\bin\\XSI.exe"=
"C:\\Program Files\\Common Files\\Adobe\\CS4ServiceManager\\CS4ServiceManager.exe"=
"C:\\Program Files\\Common Files\\AOL\\Loader\\aolload.exe"=
"C:\\Program Files\\Pando Networks\\Media Booster\\PMB.exe"=
"C:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"C:\\Program Files\\iTunes\\iTunes.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"5353:TCP"= 5353:TCP:*:Disabled:Adobe CSI CS4
"57605:TCP"= 57605:TCP:Pando Media Booster
"57605:UDP"= 57605:UDP:Pando Media Booster
"1039:TCP"= 1039:TCP:Akamai NetSession Interface
"5000:UDP"= 5000:UDP:Akamai NetSession Interface

R0 Lbd;Lbd;C:\WINDOWS\system32\drivers\Lbd.sys [8/13/2009 9:57:58 PM 64288]
R0 PCTCore;PCTools KDS;C:\WINDOWS\system32\drivers\PCTCore.sys [4/4/2010 1:28:28 PM 218592]
R1 SASDIFSV;SASDIFSV;C:\Program Files\SUPERAntiSpyware\sasdifsv.sys [2/17/2010 2:25:48 PM 12872]
R1 SASKUTIL;SASKUTIL;C:\Program Files\SUPERAntiSpyware\SASKUTIL.SYS [5/10/2010 2:41:30 PM 67656]
R2 Akamai;Akamai NetSession Interface;C:\WINDOWS\System32\svchost.exe -k Akamai [8/12/2004 10:06:49 AM 14336]
R2 Browser Defender Update Service;Browser Defender Update Service;C:\Program Files\Spyware Doctor\BDT\BDTUpdateService.exe [4/4/2010 1:30:14 PM 112592]
R2 sdAuxService;PC Tools Auxiliary Service;C:\Program Files\Spyware Doctor\pctsAuxs.exe [4/4/2010 1:28:09 PM 366840]
R2 TabletServicePen;TabletServicePen;C:\WINDOWS\system32\Pen_Tablet.exe [6/3/2010 1:25:49 PM 2749736]
R2 WTouchService;WTouch Service;C:\Program Files\WTouch\WTouchService.exe [6/3/2010 1:26:22 PM 113448]
S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe [2/4/2010 11:52:57 AM 1352832]
S3 McComponentHostService;McAfee Security Scan Component Host Service;"C:\Program Files\McAfee Security Scan\2.0.181\McCHSvc.exe" --> C:\Program Files\McAfee Security Scan\2.0.181\McCHSvc.exe [?]
S3 wacmoumonitor;Wacom Mode Helper;C:\WINDOWS\system32\drivers\wacmoumonitor.sys [6/3/2010 1:25:53 PM 15656]
S4 sptd;sptd;C:\WINDOWS\system32\drivers\sptd.sys [3/17/2009 7:26:22 PM 717296]

--- Other Services/Drivers In Memory ---

*Deregistered* - PCTSDInjDriver32

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
Akamai REG_MULTI_SZ Akamai
.
Contents of the 'Scheduled Tasks' folder

2010-10-14 C:\WINDOWS\Tasks\Ad-Aware Update (Weekly).job
- C:\Program Files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2010-02-04 15:52:58 . 2010-06-21 01:03:51]

2010-10-03 C:\WINDOWS\Tasks\AppleSoftwareUpdate.job
- C:\Program Files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 16:34:12 . 2008-07-30 16:34:12]

2010-10-20 C:\WINDOWS\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004Core.job
- C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36:00 . 2008-09-19 07:36:00]

2010-10-22 C:\WINDOWS\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004UA.job
- C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36:00 . 2008-09-19 07:36:00]
.
.
------- Supplementary Scan -------
.
IE: &AIM Toolbar Search - C:\Documents and Settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
IE: E&xport to Microsoft Excel - C:\PROGRA~1\MICROS~3\Office10\EXCEL.EXE/3000
IE: Free YouTube Download
FF - ProfilePath - C:\Documents and Settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\
FF - prefs.js: browser.search.defaulturl - hxxp://slirsredirect.search.aol.com/slirs_http/sredir?sredir=2706&invocationType=tb50fftrie7&query=
FF - prefs.js: browser.search.selectedEngine - Google
FF - prefs.js: browser.startup.homepage - hxxp://www.deviantart.com/
FF - prefs.js: keyword.URL - hxxp://search.newtabking.com/?t=1&q=
FF - plugin: C:\Documents and Settings\MegaeraJ\Local Settings\Application Data\Google\Update\1.2.183.39\npGoogleOneClick8.dll
FF - plugin: C:\Program Files\Haihaisoft Universal Player\Codec\Plugins\nppl3260.dll
FF - plugin: C:\Program Files\Haihaisoft Universal Player\Codec\Plugins\npqtplugin.dll
FF - plugin: C:\Program Files\Haihaisoft Universal Player\Codec\Plugins\nprpjplug.dll
FF - plugin: C:\Program Files\Java\jre6\bin\new_plugin\npdeployJava1.dll
FF - plugin: C:\Program Files\Pando Networks\Media Booster\npPandoWebPlugin.dll
FF - plugin: C:\Program Files\TabletPlugins\npwacom.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\WINDOWS\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbaam7a8h", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqz9s", true); // Traditional
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqs8s", true); // Simplified
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--j6w193g", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4ar", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4a87g", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7c0a67fbc", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7cvafr", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kpry57d", true); // Traditional
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kprw13d", true); // Simplified
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.ipc.plugins.enabled", false);
.
- - - - ORPHANS REMOVED - - - -

URLSearchHooks-HookURL - (no file)
URLSearchHooks-Rank - (no file)


**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-10-22 19:02:23
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes ...

scanning hidden autostart entries ...

scanning hidden files ...

scan completed successfully
hidden files: 0

**************************************************************************

Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe catchme.sys CLASSPNP.SYS disk.sys PCTCore.sys ACPI.sys hal.dll >>UNKNOWN [0x86702446]<<
kernel: MBR read successfully
detected MBR rootkit hooks:
\Driver\Disk -> CLASSPNP.SYS @ 0xf7675f28
\Driver\ACPI -> ACPI.sys @ 0xf74e8cb8
\Driver\atapi -> atapi.sys @ 0xf7480852
IoDeviceObjectType -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
\Device\Harddisk0\DR0 -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
NDIS: Dell Wireless 1390 WLAN Mini-Card -> SendCompleteHandler -> NDIS.sys @ 0xf735ebb0
PacketIndicateHandler -> NDIS.sys @ 0xf736ba21
SendHandler -> NDIS.sys @ 0xf734987b
user & kernel MBR OK

**************************************************************************
.
--------------------- DLLs Loaded Under Running Processes ---------------------

- - - - - - - > 'winlogon.exe'(704)
C:\Program Files\SUPERAntiSpyware\SASWINLO.DLL
C:\Program Files\Common Files\Adobe\Adobe Drive CS4\AdobeDriveCS4_NP.dll
C:\WINDOWS\System32\BCMLogon.dll

- - - - - - - > 'explorer.exe'(3160)
C:\Program Files\Spyware Doctor\pctgmhk.dll
C:\WINDOWS\system32\WPDShServiceObj.dll
C:\WINDOWS\system32\PortableDeviceTypes.dll
C:\WINDOWS\system32\PortableDeviceApi.dll
C:\Program Files\Common Files\Adobe\Adobe Drive CS4\AdobeDriveCS4_NP.dll
.
Completion time: 2010-10-22 19:21:57
ComboFix-quarantined-files.txt 2010-10-22 23:21:38
ComboFix2.txt 2010-10-21 19:06:32
ComboFix3.txt 2010-10-21 06:32:55

Pre-Run: 93,062,311,936 bytes free
Post-Run: 93,069,959,168 bytes free

- - End Of File - - 34CD891F78FA8E945D444883B06A9E1F
 
Hello,

Does Prevx usually take a really long time to scan? It started the learning scan about a half an hour ago and it still says 0%.
 
Hello,

So far I've had no luck in getting Prevx to work. I've restarted the computer a couple of times. I tried uninstalling and reinstalling it a few times. I also tried re-downloading the file.

One of the scans detected about 3 billion bad files in the first second before stopping (at 0%) And the most recent scan stopped at about -2 billion percent progress. Admittedly, conceptualizing what exactly -2 billion percent progress is has been pretty entertaining.
 
Other than the prevx issue, are you having any other issues? Do you have any cd emulation software installed like alcohol 120 or daemon tools? any program that can mount a cd image? I think you have software installed that is making combofix think you have a mbr infection as running mbr.exe shows you are fine.
 
Ah, I did have Daemon Tools installed. I uninstalled it and ran ComboFix again.

Here is the log:

ComboFix 10-10-23.01 - MegaeraJ 10/23/2010 23:45:29.4.2 - x86
Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.1022.566 [GMT -4:00]
Running from: c:\combofix\ComboFix.exe
Command switches used :: ComboFix
* Created a new restore point
.

((((((((((((((((((((((((( Files Created from 2010-09-24 to 2010-10-24 )))))))))))))))))))))))))))))))
.

2010-10-23 21:30 . 2010-10-23 21:30 70192 ----a-w- c:\windows\system32\PxSecure.dll
2010-10-23 21:30 . 2010-10-23 21:30 30320 ----a-w- c:\windows\system32\drivers\pxscan.sys
2010-10-23 21:30 . 2010-10-23 21:30 24400 ----a-w- c:\windows\system32\drivers\pxkbf.sys
2010-10-23 12:46 . 2010-10-23 20:51 -------- d-----w- c:\documents and settings\NetworkService\Local Settings\Application Data\Adobe
2010-10-23 02:53 . 2010-10-23 02:53 74752 ----a-w- c:\windows\system32\drivers\pxrts.sys
2010-10-23 02:53 . 2010-10-23 02:53 -------- d-----w- c:\program files\Prevx
2010-10-23 02:53 . 2010-10-23 21:30 -------- d-----w- c:\documents and settings\All Users\Application Data\PrevxCSI
2010-10-22 22:32 . 2010-10-22 22:32 -------- d-----w- c:\program files\CCleaner
2010-10-22 04:19 . 2010-10-22 04:19 -------- d-----w- c:\documents and settings\MegaeraJ\Application Data\SUPERAntiSpyware.com
2010-10-22 04:19 . 2010-10-22 04:19 -------- d-----w- c:\documents and settings\All Users\Application Data\SUPERAntiSpyware.com
2010-10-22 04:19 . 2010-10-22 04:19 -------- d-----w- c:\program files\SUPERAntiSpyware
2010-10-21 19:06 . 2010-10-21 19:06 -------- d-s---w- c:\documents and settings\NetworkService\UserData
2010-10-21 04:51 . 2010-10-21 04:51 -------- d-----w- c:\documents and settings\LocalService\Application Data\McAfee
2010-10-20 22:48 . 2010-10-20 22:48 388096 ----a-r- c:\documents and settings\MegaeraJ\Application Data\Microsoft\Installer\{45A66726-69BC-466B-A7A4-12FCBA4883D7}\HiJackThis.exe
2010-10-20 22:48 . 2010-10-20 22:48 -------- d-----w- c:\program files\Trend Micro
2010-10-20 21:53 . 2010-10-20 21:53 12872 ----a-w- c:\windows\system32\bootdelete.exe
2010-10-20 21:36 . 2010-10-20 21:36 16968 ----a-w- c:\windows\system32\drivers\hitmanpro35.sys
2010-10-20 21:36 . 2010-10-20 21:36 -------- d-----w- c:\program files\Hitman Pro 3.5
2010-10-20 21:35 . 2010-10-20 21:53 -------- d-----w- c:\documents and settings\All Users\Application Data\Hitman Pro
2010-10-14 01:54 . 2010-09-18 06:53 974848 -c----w- c:\windows\system32\dllcache\mfc42.dll
2010-10-14 01:54 . 2010-09-18 06:53 953856 -c----w- c:\windows\system32\dllcache\mfc40u.dll
2010-10-14 01:54 . 2010-08-23 16:12 617472 -c----w- c:\windows\system32\dllcache\comctl32.dll
2010-10-11 03:54 . 2010-10-11 03:54 -------- d-----w- c:\program files\Common Files\Java
2010-10-11 03:54 . 2010-07-17 09:00 423656 ----a-w- c:\windows\system32\deployJava1.dll
2010-10-11 03:54 . 2010-07-17 09:00 423656 ----a-w- c:\program files\Mozilla Firefox\plugins\npdeployJava1.dll
2010-10-11 03:45 . 2010-10-11 03:45 -------- d-----w- c:\documents and settings\All Users\Application Data\McAfee
2010-10-11 03:42 . 2010-10-21 01:18 16856 ----a-w- c:\program files\Mozilla Firefox\plugin-container.exe
2010-10-11 03:42 . 2010-10-21 01:18 719832 ----a-w- c:\program files\Mozilla Firefox\mozcpp19.dll
2010-10-05 04:43 . 2010-04-29 19:39 38224 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-10-05 04:43 . 2010-04-29 19:39 20952 ----a-w- c:\windows\system32\drivers\mbam.sys

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-09-18 16:23 . 2004-08-12 13:59 974848 ----a-w- c:\windows\system32\mfc42u.dll
2010-09-18 06:53 . 2004-08-12 13:59 974848 ----a-w- c:\windows\system32\mfc42.dll
2010-09-18 06:53 . 2004-08-12 13:59 954368 ----a-w- c:\windows\system32\mfc40.dll
2010-09-18 06:53 . 2004-08-12 13:59 953856 ----a-w- c:\windows\system32\mfc40u.dll
2010-09-09 14:16 . 2004-08-12 14:09 667136 ----a-w- c:\windows\system32\wininet.dll
2010-09-09 14:16 . 2004-08-12 14:07 61952 ----a-w- c:\windows\system32\tdc.ocx
2010-09-09 14:16 . 2004-08-12 13:58 81920 ----a-w- c:\windows\system32\ieencode.dll
2010-09-08 16:49 . 2004-08-12 13:57 369664 ----a-w- c:\windows\system32\html.iec
2010-09-08 15:17 . 2010-09-08 15:17 94208 ----a-w- c:\windows\system32\QuickTimeVR.qtx
2010-09-08 15:17 . 2010-09-08 15:17 69632 ----a-w- c:\windows\system32\QuickTime.qts
2010-09-01 11:51 . 2004-08-12 13:55 285824 ----a-w- c:\windows\system32\atmfd.dll
2010-08-31 13:42 . 2004-08-12 14:09 1852800 ----a-w- c:\windows\system32\win32k.sys
2010-08-27 08:02 . 2004-08-12 14:07 119808 ----a-w- c:\windows\system32\t2embed.dll
2010-08-27 05:57 . 2004-08-12 14:06 99840 ----a-w- c:\windows\system32\srvsvc.dll
2010-08-26 13:39 . 2004-08-12 14:06 357248 ----a-w- c:\windows\system32\drivers\srv.sys
2010-08-26 12:52 . 2009-04-16 00:21 5120 ----a-w- c:\windows\system32\xpsp4res.dll
2010-08-23 16:12 . 2004-08-12 13:56 617472 ----a-w- c:\windows\system32\comctl32.dll
2010-08-17 13:17 . 2004-08-12 14:06 58880 ----a-w- c:\windows\system32\spoolsv.exe
2010-08-16 08:45 . 2004-08-12 14:04 590848 ----a-w- c:\windows\system32\rpcrt4.dll
2010-08-05 22:32 . 2010-08-05 22:32 967 ----a-w- c:\windows\ScUnin.pif
2010-08-05 22:32 . 2010-08-05 22:32 68096 ----a-w- c:\windows\ScUnin.exe
2010-07-27 22:44 . 2010-07-27 22:44 91424 ----a-w- c:\windows\system32\dnssd.dll
2010-07-27 22:44 . 2010-07-27 22:44 107808 ----a-w- c:\windows\system32\dns-sd.exe
2010-04-15 22:30 . 2010-04-15 22:23 940197287 ----a-w- c:\program files\FEZsetup_2010-04-01.exe
.

((((((((((((((((((((((((((((( SnapShot@2010-10-21_06.27.12 )))))))))))))))))))))))))))))))))))))))))
.
+ 2010-10-23 22:01 . 2010-10-23 22:01 16384 c:\windows\Temp\Perflib_Perfdata_790.dat
+ 2010-10-23 22:01 . 2010-10-23 22:01 16384 c:\windows\Temp\Perflib_Perfdata_6dc.dat
+ 2010-10-23 06:22 . 2010-10-23 06:22 16384 c:\windows\Temp\Perflib_Perfdata_110.dat
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]
"SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\SUPERAntiSpyware.exe" [2010-09-28 2424560]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"dla"="c:\windows\system32\dla\tfswctrl.exe" [2004-08-13 122939]
"Broadcom Wireless Manager UI"="c:\windows\system32\WLTRAY.exe" [2007-03-16 1392640]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2006-05-01 7561216]
"nwiz"="nwiz.exe" [2006-05-01 1519616]
"NVHotkey"="nvHotkey.dll" [2006-05-01 73728]
"SigmatelSysTrayApp"="c:\program files\SigmaTel\C-Major Audio\WDM\stsystra.exe" [2007-05-10 405504]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2006-03-08 761947]
"ISTray"="c:\program files\Spyware Doctor\pctsTray.exe" [2010-05-27 1287120]

c:\documents and settings\All Users\Start Menu\Programs\Startup\
TabUserW.exe.lnk - c:\windows\system32\WTablet\TabUserW.exe [2008-8-1 140848]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "c:\program files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 77824]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2009-09-03 22:21 548352 ----a-w- c:\program files\SUPERAntiSpyware\SASWINLO.DLL

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-06-20 02:04 35760 ----a-w- c:\program files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\DVDLauncher]
2004-10-12 20:54 57344 ------w- c:\program files\CyberLink\PowerDVD\DVDLauncher.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Google Update]
2008-09-19 07:36 133104 ----atw- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2010-09-24 06:10 421160 ----a-w- c:\program files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-09-08 15:17 421888 ----a-w- c:\program files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\UpdateManager]
2004-01-07 05:01 110592 ----a-w- c:\program files\Common Files\Sonic\Update Manager\sgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\manager.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\monitor.exe"=
"c:\\Program Files\\Autodesk\\Backburner\\server.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\support\\bin\\win\\RosettaStoneLtdServices.exe"=
"c:\\Program Files\\Rosetta Stone\\Rosetta Stone Version 3\\RosettaStoneVersion3.exe"=
"c:\\Program Files\\DNA\\btdna.exe"=
"c:\\Program Files\\AIM6\\aim6.exe"=
"c:\\Softimage\\XSI_5.11\\Application\\bin\\XSI.exe"=
"c:\\Program Files\\Common Files\\Adobe\\CS4ServiceManager\\CS4ServiceManager.exe"=
"c:\\Program Files\\Common Files\\AOL\\Loader\\aolload.exe"=
"c:\\Program Files\\Pando Networks\\Media Booster\\PMB.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Prevx\\prevx.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"5353:TCP"= 5353:TCP:*:Disabled:Adobe CSI CS4
"57605:TCP"= 57605:TCP:Pando Media Booster
"57605:UDP"= 57605:UDP:Pando Media Booster
"1041:TCP"= 1041:TCP:Akamai NetSession Interface
"5000:UDP"= 5000:UDP:Akamai NetSession Interface

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [8/13/2009 9:57 PM 64288]
R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [4/4/2010 1:28 PM 218592]
R0 pxscan;pxscan;c:\windows\system32\drivers\pxscan.sys [10/23/2010 5:30 PM 30320]
R1 pxrts;pxrts;c:\windows\system32\drivers\pxrts.sys [10/22/2010 10:53 PM 74752]
R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [2/17/2010 2:25 PM 12872]
R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [5/10/2010 2:41 PM 67656]
R2 Akamai;Akamai NetSession Interface;c:\windows\System32\svchost.exe -k Akamai [8/12/2004 10:06 AM 14336]
R2 Browser Defender Update Service;Browser Defender Update Service;c:\program files\Spyware Doctor\BDT\BDTUpdateService.exe [4/4/2010 1:30 PM 112592]
R2 CSIScanner;CSIScanner;c:\program files\Prevx\prevx.exe [10/22/2010 10:53 PM 6407216]
R2 sdAuxService;PC Tools Auxiliary Service;c:\program files\Spyware Doctor\pctsAuxs.exe [4/4/2010 1:28 PM 366840]
R2 TabletServicePen;TabletServicePen;c:\windows\system32\Pen_Tablet.exe [6/3/2010 1:25 PM 2749736]
R2 WTouchService;WTouch Service;c:\program files\WTouch\WTouchService.exe [6/3/2010 1:26 PM 113448]
R3 pxkbf;pxkbf;c:\windows\system32\drivers\pxkbf.sys [10/23/2010 5:30 PM 24400]
S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [2/4/2010 11:52 AM 1352832]
S3 McComponentHostService;McAfee Security Scan Component Host Service;"c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe" --> c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe [?]
S3 wacmoumonitor;Wacom Mode Helper;c:\windows\system32\drivers\wacmoumonitor.sys [6/3/2010 1:25 PM 15656]
S4 sptd;sptd;c:\windows\system32\drivers\sptd.sys [3/17/2009 7:26 PM 717296]

--- Other Services/Drivers In Memory ---

*Deregistered* - PCTSDInjDriver32

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
Akamai REG_MULTI_SZ Akamai
.
Contents of the 'Scheduled Tasks' folder

2010-10-14 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2010-02-04 01:03]

2010-10-03 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 16:34]

2010-10-20 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004Core.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]

2010-10-23 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-746137067-583907252-682003330-1004UA.job
- c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2008-09-19 07:36]
.
.
------- Supplementary Scan -------
.
IE: &AIM Toolbar Search - c:\documents and settings\All Users\Application Data\AIM Toolbar\ieToolbar\resources\en-US\local\search.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~3\Office10\EXCEL.EXE/3000
IE: Free YouTube Download
FF - ProfilePath - c:\documents and settings\MegaeraJ\Application Data\Mozilla\Firefox\Profiles\ll0zv9uq.default\
FF - prefs.js: browser.search.defaulturl - hxxp://slirsredirect.search.aol.com/slirs_http/sredir?sredir=2706&invocationType=tb50fftrie7&query=
FF - prefs.js: browser.search.selectedEngine - Google
FF - prefs.js: browser.startup.homepage - hxxp://www.deviantart.com/
FF - prefs.js: keyword.URL - hxxp://search.newtabking.com/?t=1&q=
FF - plugin: c:\documents and settings\MegaeraJ\Local Settings\Application Data\Google\Update\1.2.183.39\npGoogleOneClick8.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nppl3260.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\npqtplugin.dll
FF - plugin: c:\program files\Haihaisoft Universal Player\Codec\Plugins\nprpjplug.dll
FF - plugin: c:\program files\Java\jre6\bin\new_plugin\npdeployJava1.dll
FF - plugin: c:\program files\Pando Networks\Media Booster\npPandoWebPlugin.dll
FF - plugin: c:\program files\TabletPlugins\npwacom.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbaam7a8h", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqz9s", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--fiqs8s", true); // Simplified
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--j6w193g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4ar", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgberp4a5d4a87g", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7c0a67fbc", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--mgbqly7cvafr", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kpry57d", true); // Traditional
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.IDN.whitelist.xn--kprw13d", true); // Simplified
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.ipc.plugins.enabled", false);
.
- - - - ORPHANS REMOVED - - - -

URLSearchHooks-HookURL - (no file)
URLSearchHooks-Rank - (no file)


**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-10-24 00:02
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes ...

scanning hidden autostart entries ...

scanning hidden files ...

scan completed successfully
hidden files: 0

**************************************************************************

Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe catchme.sys CLASSPNP.SYS disk.sys PCTCore.sys ACPI.sys hal.dll >>UNKNOWN [0x866EB446]<<
kernel: MBR read successfully
detected MBR rootkit hooks:
\Driver\Disk -> CLASSPNP.SYS @ 0xf7675f28
\Driver\ACPI -> ACPI.sys @ 0xf74e8cb8
\Driver\atapi -> atapi.sys @ 0xf7480852
IoDeviceObjectType -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
\Device\Harddisk0\DR0 -> DeleteProcedure -> ntkrnlpa.exe @ 0x805836a8
ParseProcedure -> ntkrnlpa.exe @ 0x805827e8
NDIS: Dell Wireless 1390 WLAN Mini-Card -> SendCompleteHandler -> NDIS.sys @ 0xf735ebb0
PacketIndicateHandler -> NDIS.sys @ 0xf736ba21
SendHandler -> NDIS.sys @ 0xf734987b
user & kernel MBR OK

**************************************************************************
.
--------------------- DLLs Loaded Under Running Processes ---------------------

- - - - - - - > 'winlogon.exe'(736)
c:\program files\SUPERAntiSpyware\SASWINLO.DLL
c:\program files\Common Files\Adobe\Adobe Drive CS4\AdobeDriveCS4_NP.dll
c:\windows\System32\BCMLogon.dll

- - - - - - - > 'explorer.exe'(3844)
c:\program files\Spyware Doctor\pctgmhk.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
c:\program files\Common Files\Adobe\Adobe Drive CS4\AdobeDriveCS4_NP.dll
.
Completion time: 2010-10-24 00:06:55
ComboFix-quarantined-files.txt 2010-10-24 04:06
ComboFix2.txt 2010-10-22 23:22
ComboFix3.txt 2010-10-21 19:06
ComboFix4.txt 2010-10-21 06:32

Pre-Run: 116,002,459,648 bytes free
Post-Run: 116,175,499,264 bytes free

- - End Of File - - 30C50097AF6DCE0AAF4EFE8BAF29FF89
 
Back
Top