microsoft security essentials

ok so my other computer is back from repairing, the thing is, it has a virus protection called microsoft securit essentials and it shows in history that it has decteded and deleted all of the viruses except for 1 witch is quarantide.
everytime when i want to update it says that microsoft security essentials wasnt abel to check for virus and spyware defenition updates, make sure your computer is connected to the interent and try again
and also when looking at the virust defition version it says 1.79.1994 also same for spyware.
is it a bad virus protection, if so, what should i use then?
 
Sounds like your still infected. Install malwarebytes and see if it will update, it not, then you are still infected. Follow this procedure.

Download and Run ComboFix
If you already have Combofix, please delete this copy and download it again as it's being updated regularly.
Note: Do not mouseclick combofix's window whilst it's running. That may cause it to stall

Combofix should never take more that 20 minutes including the reboot if malware is detected.
If it does, open Task Manager then Processes tab (press ctrl, alt and del at the same time) and end any processes of findstr, find, sed or swreg, then combofix should continue.
If that happened we want to know, and also what process you had to end.

In your next reply please post:
  • The ComboFix log
  • A fresh HiJackThis log
  • An update on how your computer is running
 
whoops, i accidently didint see that u said that i will download MW bytes antimaleware to see if it updates so i did combofix before installing amlewarebytes
anyway, i havent hijacklogged yet, but combofix deleted some files and made a log.
o, and maleware bytes updated.
 
but still, microsoft security essentrials wont update....and automatic updates are turned off and windows said that it cannot turn it on at this time..bullocks.
 
hijackthis log...
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
c:\Program Files\Microsoft Security Essentials\MsMpEng.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\CTsvcCDA.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\system32\PnkBstrA.exe
C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
C:\Program Files\Google\Update\1.2.183.23\GoogleCrashHandler.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\wscntfy.exe
C:\WINDOWS\SOUNDMAN.EXE
C:\Program Files\Common Files\Java\Java Update\jusched.exe
C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe
C:\Program Files\Microsoft Security Essentials\msseces.exe
C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe
C:\Program Files\DAEMON Tools Lite\daemon.exe
C:\Program Files\OpenOffice.org 2.4\program\soffice.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\OpenOffice.org 2.4\program\soffice.BIN
C:\Program Files\Mozilla Firefox\firefox.exe
C:\WINDOWS\system32\msiexec.exe
C:\Program Files\Trend Micro\HiJackThis\HiJackThis.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.neti.ee/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: (no name) - {34123098-D81D-471D-AA97-37B110718A42} - C:\WINDOWS\system32\tuvVPhIB.dll (file missing)
O2 - BHO: WormRadar.com IESiteBlocker.NavFilter - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - (no file)
O2 - BHO: Windows Live Family Safety Browser Helper - {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - C:\Program Files\Windows Live\Family Safety\fssbho.dll
O2 - BHO: Click-to-Call BHO - {5C255C8A-E604-49b4-9D64-90988571CECB} - C:\Program Files\Windows Live\Messenger\wlchtc.dll
O2 - BHO: Search Helper - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: (no name) - {BA8FBC1F-CB33-46CA-BA88-48A3988ED988} - C:\WINDOWS\system32\byXPIyvW.dll (file missing)
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: Windows Live Toolbar Helper - {E15A8DC0-8516-42A1-81EA-DC94EC1ACF10} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: &Windows Live Toolbar - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O4 - HKLM\..\Run: [SoundMan] SOUNDMAN.EXE
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [CTCheck] C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [MSSE] "c:\Program Files\Microsoft Security Essentials\msseces.exe" -hide -runkey
O4 - HKCU\..\Run: [MsnMsgr] "C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe" /background
O4 - HKCU\..\Run: [DAEMON Tools Lite] "C:\Program Files\DAEMON Tools Lite\daemon.exe" -autorun
O4 - HKCU\..\Run: [EA Core] "C:\Program Files\Electronic Arts\EADM\Core.exe" -silent
O4 - HKCU\..\RunOnce: [Shockwave Updater] C:\WINDOWS\system32\Adobe\Shockwave 11\SwHelper_1150595.exe -Update -1150595 -"Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 5.1; FLV; .NET CLR 2.0.50727; .NET CLR 1.1.4322; .NET CLR 3.0.04506.30; .NET CLR 3.0.4506.2152; .NET CLR 3.5.30729; Creative ZENcast v2.00.13)" -"http://www.miniclip.com/games/world-soccer/en/"
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - Startup: OpenOffice.org 2.4.lnk = C:\Program Files\OpenOffice.org 2.4\program\quickstart.exe
O8 - Extra context menu item: Google Sidewiki... - res://C:\Program Files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_96D6FF0C6D236BF8.dll/cmsidewiki.html
O9 - Extra button: Blog This - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: &Blog This in Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {0CCA191D-13A6-4E29-B746-314DEE697D83} (Facebook Photo Uploader 5 Control) - http://upload.facebook.com/controls/2008.10.10_v5.5.8/FacebookPhotoUploader5.cab
O16 - DPF: {4BFD075D-C36E-4F28-BB0A-5D472795197A} (PowerLoader Class) - http://www.powerchallenge.com/applet/PowerLoader.cab
O16 - DPF: {4F1E5B1A-2A80-42CA-8532-2D05CB959537} (MSN Photo Upload Tool) - http://gfx1.hotmail.com/mail/w3/resources/MSNPUpld.cab
O16 - DPF: {6C269571-C6D7-4818-BCA4-32A035E8C884} (Creative Software AutoUpdate) - http://www.creative.com/softwareupdate/su/ocx/15101/CTSUEng.cab
O16 - DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} (Battlefield Heroes Updater) - https://www.battlefieldheroes.com/static/updater/BFHUpdater_4.0.21.0.cab
O16 - DPF: {917623D1-D8E5-11D2-BE8B-00104B06BDE3} (CamImage Class) - http://gw.tallinnlv.ee:11082/activex/AxisCamControl.cab
O16 - DPF: {EA6246B4-F380-443F-8727-9AEA3371146C} (CPlayFirstWeddingDashControl Object) - http://cdn.ll.neoedge.com/webgames/WeddingDash/WeddingDash.1.0.0.47.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/softwareupdate/su/ocx/15106/CTPID.cab
O18 - Protocol: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - (no file)
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O20 - Winlogon Notify: avgrsstarter - avgrsstx.dll (file missing)
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Creative Service for CDROM Access - Creative Technology Ltd - C:\WINDOWS\system32\CTsvcCDA.exe
O23 - Service: Google Update Service (gupdate) (gupdate) - Google Inc. - C:\Program Files\Google\Update\GoogleUpdate.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: PnkBstrA - Unknown owner - C:\WINDOWS\system32\PnkBstrA.exe
O23 - Service: Remote Procedure Call (HNM) (RPCER) - Unknown owner - C:\Program Files\Common Files\ODBC\comp.exe (file missing)

--
End of file - 8542 bytes
 
Combofix log..
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

C:\Documents and Settings\Kasutaja\Application Data\bcrypt.html
C:\Documents and Settings\Kasutaja\Recent\Thumbs.db
C:\Documents and Settings\Kasutaja\Start Menu\Programs\Startup\MagicDisc.lnk
C:\RECYCLER\S-1-5-21-0884362995-4147922285-207270745-6595
C:\RECYCLER\S-1-5-21-1038972821-5730077182-734653730-0083
C:\RECYCLER\S-1-5-21-2707077466-8384637612-412975894-7637
C:\RECYCLER\S-1-5-21-2889911231-0967414241-302042977-0556
C:\RECYCLER\S-1-5-21-6007279826-6947162767-525719023-2220
C:\RECYCLER\S-1-5-21-7283134393-6831713111-350260814-8543
C:\RECYCLER\S-1-5-21-7927244178-5823323494-938281343-5892
C:\Thumbs.db
C:\WINDOWS\Downloaded Program Files\f3initialsetup1.0.1.1.inf
C:\WINDOWS\Downloaded Program Files\popcaploader.inf
C:\WINDOWS\system32\28455546.exe
C:\WINDOWS\system32\BIhPVvut.ini
C:\WINDOWS\system32\BIhPVvut.ini2
C:\WINDOWS\system32\cfskbdka.ini
C:\WINDOWS\system32\fcvqvlxg.ini
C:\WINDOWS\system32\Thumbs.db
C:\WINDOWS\system32\WvyIPXyb.ini
C:\WINDOWS\system32\WvyIPXyb.ini2

.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.

-------\Legacy_6TO4
-------\Legacy_IAS
-------\Legacy_MYWEBSEARCHSERVICE
-------\Service_6to4
-------\Service_Ias
-------\Service_NETSVCS_0x0


((((((((((((((((((((((((( Files Created from 2010-03-25 to 2010-04-25 )))))))))))))))))))))))))))))))
.

2010-04-16 15:12:53 . 2010-04-16 15:13:23 -------- d-----w- C:\Program Files\Microsoft Security Essentials
2010-04-16 12:10:03 . 2010-04-12 14:29:19 411368 ----a-w- C:\WINDOWS\system32\deployJava1.dll
2010-04-15 13:39:14 . 2010-04-15 13:39:14 -------- d-----w- C:\found.000

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-04-25 16:48:12 . 2008-11-12 19:38:00 -------- d-----w- C:\Documents and Settings\Kasutaja\Application Data\OpenOffice.org2
2010-04-25 15:54:02 . 2008-08-05 14:35:20 -------- d-----w- C:\Documents and Settings\Kasutaja\Application Data\uTorrent
2010-04-16 12:10:38 . 2008-08-07 20:24:34 -------- d-----w- C:\Program Files\Common Files\Java
2010-04-16 12:10:28 . 2010-04-16 12:10:28 503808 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\msvcp71.dll
2010-04-16 12:10:28 . 2010-04-16 12:10:28 499712 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\jmc.dll
2010-04-16 12:10:28 . 2010-04-16 12:10:28 348160 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\msvcr71.dll
2010-04-16 12:10:26 . 2010-04-16 12:10:26 61440 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\17\6d0ad391-309a437f-n\decora-sse.dll
2010-04-16 12:10:26 . 2010-04-16 12:10:26 12800 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\17\6d0ad391-309a437f-n\decora-d3d.dll
2010-04-16 12:09:53 . 2008-08-07 20:25:05 -------- d-----w- C:\Program Files\Java
2010-04-16 11:44:51 . 2008-11-01 12:14:09 -------- d-----w- C:\Program Files\Malwarebytes' Anti-Malware
2010-04-16 11:44:26 . 2009-04-19 12:31:39 5918776 ----a-w- C:\Documents and Settings\All Users\Application Data\Malwarebytes\Malwarebytes' Anti-Malware\mbam-setup.exe
2010-04-16 11:40:42 . 2008-08-11 06:35:07 -------- d-----w- C:\Documents and Settings\All Users\Application Data\Avg8
2010-04-16 11:16:23 . 2008-10-14 19:58:54 -------- d-----w- C:\Program Files\Common Files\Apple
2010-03-30 16:06:27 . 2008-09-06 17:18:46 -------- d---a-w- C:\Documents and Settings\All Users\Application Data\TEMP
2010-03-29 21:46:30 . 2008-11-01 12:14:10 38224 ----a-w- C:\WINDOWS\system32\drivers\mbamswissarmy.sys
2010-03-29 21:45:52 . 2008-11-01 12:14:12 20824 ----a-w- C:\WINDOWS\system32\drivers\mbam.sys
2010-03-27 10:04:31 . 2008-08-05 14:35:32 -------- d-----w- C:\Documents and Settings\Kasutaja\Application Data\Sports Interactive
2010-03-24 20:38:02 . 2009-12-04 16:03:27 -------- d-----w- C:\Program Files\Death Rally
2010-03-21 22:25:08 . 2009-01-08 13:10:19 -------- d-----w- C:\Program Files\Safari
2010-03-21 22:21:43 . 2010-03-21 22:21:43 79144 ----a-w- C:\Documents and Settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.22.7\SetupAdmin.exe
2010-03-20 14:38:16 . 2010-03-20 14:38:10 -------- d-----w- C:\Program Files\Mozilla
2010-03-19 20:42:24 . 2008-08-18 12:00:38 -------- d-----w- C:\Program Files\uTorrent
2010-03-19 05:27:11 . 2008-12-01 12:32:33 -------- d-----w- C:\Program Files\GUNROX
2010-03-18 15:30:45 . 2008-08-07 20:12:13 -------- d-----w- C:\Program Files\Google
2010-03-18 14:54:23 . 2008-08-07 20:22:29 -------- d-----w- C:\Program Files\LimeWire
2010-03-18 14:53:31 . 2009-10-30 19:34:35 -------- d-----w- C:\Program Files\Glest_3.2.2
2010-03-18 14:52:35 . 2009-05-21 12:16:12 -------- d-----w- C:\Documents and Settings\All Users\Application Data\Electronic Arts
2010-03-18 14:52:35 . 2008-09-16 06:09:52 -------- d-----w- C:\Program Files\Electronic Arts
2010-03-18 14:50:13 . 2008-08-05 11:47:45 -------- d--h--w- C:\Program Files\InstallShield Installation Information
2010-03-18 14:42:50 . 2008-08-31 22:05:54 -------- d--h--w- C:\Documents and Settings\Kasutaja\Application Data\yahoo!
2010-03-18 14:42:50 . 2008-08-31 19:13:54 -------- d-----w- C:\Documents and Settings\All Users\Application Data\Yahoo!
2010-03-18 14:41:22 . 2008-08-31 13:02:24 -------- d-----w- C:\Program Files\AIM
2010-03-18 14:41:18 . 2008-08-31 13:03:48 -------- d-----w- C:\Documents and Settings\Kasutaja\Application Data\Aim
2010-03-15 04:56:53 . 2008-11-07 05:12:43 -------- d-----w- C:\Program Files\Eidos Interactive
2010-03-11 21:56:16 . 2008-11-12 19:40:59 1 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\OpenOffice.org2\user\uno_packages\cache\stamp.sys
2010-03-10 13:52:13 . 2009-09-04 14:54:56 69 ----a-w- C:\Documents and Settings\Kasutaja\jagex_runescape_preferences2.dat
2010-03-10 13:50:03 . 2008-10-03 12:30:36 41 ----a-w- C:\Documents and Settings\Kasutaja\jagex_runescape_preferences.dat
2010-03-10 13:30:09 . 2008-11-21 22:00:12 -------- d-----w- C:\Program Files\EA SPORTS
2010-03-09 17:44:53 . 2009-01-20 17:19:53 -------- d-----w- C:\Documents and Settings\All Users\Application Data\Sports Interactive
2010-03-08 18:46:34 . 2009-07-14 12:11:26 -------- d-----w- C:\Program Files\Sports Interactive
2010-03-08 09:25:38 . 2009-03-01 15:02:10 -------- d-----w- C:\Documents and Settings\Kasutaja\Application Data\U3
2010-03-07 11:05:14 . 2010-03-07 11:05:14 -------- d-----w- C:\Program Files\GDS
2010-02-27 06:54:33 . 2009-06-17 07:17:51 -------- d-----w- C:\Program Files\Rockstar Games
2010-02-25 17:07:29 . 2010-02-25 17:05:31 43520 ----a-w- C:\WINDOWS\system32\CmdLineExt03.dll
2010-02-20 19:22:16 . 2009-09-24 04:48:55 24104 ----a-w- C:\WINDOWS\system32\GDIPFONTCACHEV1.DAT
2010-02-16 14:43:03 . 2010-02-16 14:43:03 79144 ----a-w- C:\Documents and Settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.21.10\SetupAdmin.exe
2010-02-05 16:28:42 . 2009-12-05 16:57:20 79488 ----a-w- C:\Documents and Settings\Kasutaja\Application Data\Sun\Java\jre1.6.0_17\gtapi.dll
2009-07-14 00:16:26 . 2009-07-14 00:16:26 1044480 ----a-w- C:\Program Files\mozilla firefox\plugins\libdivx.dll
2009-07-14 00:16:26 . 2009-07-14 00:16:26 200704 ----a-w- C:\Program Files\mozilla firefox\plugins\ssldivx.dll
2002-07-31 16:55:12 . 2009-06-22 14:37:49 106 -csh--w- C:\WINDOWS\WSYS049.SYS
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"MsnMsgr"="C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe" [2009-07-26 13:44:34 3883856]
"DAEMON Tools Lite"="C:\Program Files\DAEMON Tools Lite\daemon.exe" [2008-12-29 10:40:30 687560]

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\RunOnce]
"Shockwave Updater"="C:\WINDOWS\system32\Adobe\Shockwave 11\SwHelper_1150595.exe" [2009-03-19 15:55:14 460216]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SoundMan"="SOUNDMAN.EXE" [2006-11-17 02:42:52 577536]
"SunJavaUpdateSched"="C:\Program Files\Common Files\Java\Java Update\jusched.exe" [2010-02-18 08:43:18 248040]
"CTCheck"="C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe" [2007-11-06 08:08:10 397312]
"QuickTime Task"="C:\Program Files\QuickTime\qttask.exe" [2009-05-26 14:18:30 413696]
"MSSE"="c:\Program Files\Microsoft Security Essentials\msseces.exe" [2010-02-21 02:03:12 1093208]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="C:\WINDOWS\system32\CTFMON.EXE" [2008-04-14 00:12:16 15360]

C:\Documents and Settings\Kasutaja\Start Menu\Programs\Startup\
OpenOffice.org 2.4.lnk - C:\Program Files\OpenOffice.org 2.4\program\quickstart.exe [2008-5-30 393216]

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\MsMpSvc]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\EnableDCOM]
N [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\restrictanonymous]
 [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\restrictanonymoussam]
 [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2008-06-11 23:38:00 34672 ----a-w- C:\Program Files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\AVG8_TRAY]
2008-11-28 07:31:12 1261336 ----a-w- C:\PROGRA~1\AVG\AVG8\avgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\CTSyncU.exe]
2007-07-17 08:03:38 868352 ------w- C:\Program Files\Creative\Sync Manager Unicode\CTSyncU.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\fssui]
2009-08-05 19:48:42 647520 ----a-w- C:\Program Files\Windows Live\Family Safety\fsui.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2008-11-20 11:20:54 290088 ----a-w- C:\Program Files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\services]
"Bonjour Service"=2 (0x2)
"avg8wd"=2 (0x2)
"avg8emc"=2 (0x2)

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"C:\\Program Files\\Messenger\\msmsgs.exe"=
"C:\\Program Files\\AVG\\AVG8\\avgemc.exe"=
"C:\\Program Files\\AVG\\AVG8\\avgupd.exe"=
"C:\\Program Files\\uTorrent\\uTorrent.exe"=
"C:\\Documents and Settings\\Kasutaja\\My Documents\\LimeWire\\Saved\\Command & Conquer Generals\\game.dat"=
"C:\\Program Files\\SecondLife\\SLVoice.exe"=
"C:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"C:\\Program Files\\EA GAMES\\Command & Conquer Generals Zero Hour\\game.dat"=
"C:\\WINDOWS\\system32\\PnkBstrA.exe"=
"C:\\WINDOWS\\system32\\PnkBstrB.exe"=
"C:\\Program Files\\EA GAMES\\Command and Conquer Generals\\game.dat"=
"C:\\Program Files\\iTunes\\iTunes.exe"=
"C:\\Program Files\\Java\\jre6\\bin\\java.exe"=
"C:\\Program Files\\EA GAMES\\Command and Conquer Generals\\patchget.dat"=
"C:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"C:\\Program Files\\Windows Live\\Sync\\WindowsLiveSync.exe"=
"C:\\Program Files\\Skype\\Plugin Manager\\skypePM.exe"=
"C:\\Program Files\\Skype\\Phone\\Skype.exe"=
"C:\\Documents and Settings\\Owner\\My Documents\\Downloads\\cnc\\Command And Conquer - Tiberian Sun + Firestorm Expansion\\game.exe"=
"C:\\Program Files\\Sports Interactive\\Football Manager 2010\\fm.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"1806:TCP"= 1806:TCP:eghxgmt

R0 sptd;sptd;C:\WINDOWS\system32\drivers\sptd.sys [10.03.2009 0:08:22 717296]
R3 PbsAuDrv;PolderbitS Audio Driver;C:\WINDOWS\system32\drivers\pbsaudrv.sys [20.12.2009 13:25:23 110752]
R3 seehcri;Sony Ericsson seehcri Device Driver;C:\WINDOWS\system32\drivers\seehcri.sys [25.11.2009 22:10:57 27632]
S2 ghkclv;Server Manager;C:\WINDOWS\system32\svchost.exe -k netsvcs [28.02.2006 15:00:00 14336]
S2 gupdate;Google Update Service (gupdate);C:\Program Files\Google\Update\GoogleUpdate.exe [21.12.2009 17:18:59 135664]
S2 RPCER;Remote Procedure Call (HNM);C:\Program Files\Common Files\ODBC\comp.exe --> C:\Program Files\Common Files\ODBC\comp.exe [?]
S3 kzixj;kzixj;\??\C:\WINDOWS\system32\03.tmp --> C:\WINDOWS\system32\03.tmp [?]
S3 liulu;liulu;\??\C:\WINDOWS\system32\013.tmp --> C:\WINDOWS\system32\013.tmp [?]
S3 ntcexkd;ntcexkd;\??\C:\WINDOWS\system32\0C.tmp --> C:\WINDOWS\system32\0C.tmp [?]
S3 qtdtknoxf;qtdtknoxf;\??\C:\WINDOWS\system32\019.tmp --> C:\WINDOWS\system32\019.tmp [?]
S3 s0016bus;Sony Ericsson Device 0016 driver (WDM);C:\WINDOWS\system32\drivers\s0016bus.sys [25.11.2009 22:06:16 89256]
S3 s0016mdfl;Sony Ericsson Device 0016 USB WMC Modem Filter;C:\WINDOWS\system32\drivers\s0016mdfl.sys [25.11.2009 22:06:16 15016]
S3 s0016mdm;Sony Ericsson Device 0016 USB WMC Modem Driver;C:\WINDOWS\system32\drivers\s0016mdm.sys [25.11.2009 22:06:16 120744]
S3 s0016mgmt;Sony Ericsson Device 0016 USB WMC Device Management Drivers (WDM);C:\WINDOWS\system32\drivers\s0016mgmt.sys [25.11.2009 22:06:19 114216]
S3 s0016nd5;Sony Ericsson Device 0016 USB Ethernet Emulation SEMC0016 (NDIS);C:\WINDOWS\system32\drivers\s0016nd5.sys [25.11.2009 22:06:17 25512]
S3 s0016obex;Sony Ericsson Device 0016 USB WMC OBEX Interface;C:\WINDOWS\system32\drivers\s0016obex.sys [25.11.2009 22:06:18 110632]
S3 s0016unic;Sony Ericsson Device 0016 USB Ethernet Emulation SEMC0016 (WDM);C:\WINDOWS\system32\drivers\s0016unic.sys [25.11.2009 22:06:19 115752]
S3 txddrdm;txddrdm;\??\C:\WINDOWS\system32\04.tmp --> C:\WINDOWS\system32\04.tmp [?]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
getPlusHelper REG_MULTI_SZ getPlusHelper

HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs
NETSVCS_0x1
NETSVCS_0x2
NETSVCS_0x3
NETSVCS_0x4
NETSVCS_0x5
NETSVCS_0x6
NETSVCS_0x7
NETSVCS_0x8
NETSVCS_0x9
NETSVCS_0xa
NETSVCS_0xb
ghkclv
.
Contents of the 'Scheduled Tasks' folder

2010-04-25 C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job
- C:\Program Files\Google\Update\GoogleUpdate.exe [2009-12-21 14:18:59 . 2009-12-21 14:18:55]

2010-04-25 C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job
- C:\Program Files\Google\Update\GoogleUpdate.exe [2009-12-21 14:18:59 . 2009-12-21 14:18:55]

2010-04-25 C:\WINDOWS\Tasks\MP Scheduled Scan.job
- c:\Program Files\Microsoft Security Essentials\MpCmdRun.exe [2009-12-09 15:02:36 . 2009-12-09 15:02:36]
.
.
------- Supplementary Scan -------
.
uStart Page = hxxp://www.neti.ee/
IE: Google Sidewiki... - C:\Program Files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_96D6FF0C6D236BF8.dll/cmsidewiki.html
DPF: {4BFD075D-C36E-4F28-BB0A-5D472795197A} - hxxp://www.powerchallenge.com/applet/PowerLoader.cab
DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} - hxxps://www.battlefieldheroes.com/static/updater/BFHUpdater_4.0.21.0.cab
FF - ProfilePath - C:\Documents and Settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\
FF - plugin: C:\Documents and Settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\extensions\{E2883E8F-472F-4fb0-9522-AC9BF37916A7}\plugins\np_gp.dll
FF - plugin: C:\Documents and Settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\extensions\[email protected]\platform\WINNT_x86-msvc\plugins\npBFHUpdater.dll
FF - plugin: C:\Documents and Settings\Kasutaja\My Documents\DivX\DivX Player\npDivxPlayerPlugin.dll
FF - plugin: C:\Documents and Settings\Kasutaja\My Documents\DivX\DivX Web Player\npdivx32.dll
FF - plugin: C:\Program Files\Google\Update\1.2.183.23\npGoogleOneClick8.dll
FF - plugin: C:\Program Files\Mozilla Firefox\plugins\npdeployJava1.dll
FF - plugin: C:\Program Files\Mozilla Firefox\plugins\NPOP7PlugIn.dll
FF - plugin: C:\Program Files\Windows Live\Photo Gallery\NPWLPG.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\WINDOWS\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("ui.use_native_colors", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("ui.use_native_popup_windows", false);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.enable_click_image_resizing", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("accessibility.browsewithcaret_shortcut.enabled", true);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("javascript.options.mem.high_water_mark", 32);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("javascript.options.mem.gc_frequency", 1600);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("network.auth.force-generic-ntlm", false);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("svg.smil.enabled", false);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("ui.trackpoint_hack.enabled", -1);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.debug", false);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.agedWeight", 2);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.bucketSize", 1);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.maxTimeGroupings", 25);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.timeGroupingSize", 604800);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.boundaryWeight", 25);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.prefixWeight", 5);
C:\Program Files\Mozilla Firefox\greprefs\all.js - pref("html5.enable", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("app.update.download.backgroundInterval", 600);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("app.update.url.manual", "http://www.firefox.com");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("browser.search.param.yahoo-fr-ja", "mozff");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.name", "chrome://browser/locale/browser.properties");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.description", "chrome://browser/locale/browser.properties");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add", "addons.mozilla.org");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add.36", "getpersonas.com");
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("lightweightThemes.update.enabled", true);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.allTabs.previews", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("plugins.hide_infobar_for_outdated_plugin", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("plugins.update.notifyUser", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("toolbar.customization.usesheet", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.enable", false);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.max", 20);
C:\Program Files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.cachetime", 20);
.
- - - - ORPHANS REMOVED - - - -

BHO-{34123098-D81D-471D-AA97-37B110718A42} - C:\WINDOWS\system32\tuvVPhIB.dll
BHO-{BA8FBC1F-CB33-46CA-BA88-48A3988ED988} - C:\WINDOWS\system32\byXPIyvW.dll
HKCU-Run-EA Core - C:\Program Files\Electronic Arts\EADM\Core.exe
Notify-avgrsstarter - avgrsstx.dll
MSConfigStartUp-Fast Encoder - C:\DOCUME~1\Kasutaja\LOCALS~1\Temp\fedhost.exe
MSConfigStartUp-hivew - C:\DOCUME~1\Kasutaja\LOCALS~1\Temp\281709843050don.dll
MSConfigStartUp-Java Runtime Enviornment - C:\WINDOWS\TEMP\C:\WINDOWS\TEMP\Update.exe
MSConfigStartUp-MicrosoftUpdate - C:\Documents and Settings\Kasutaja\Application Data\taskeng.exe
MSConfigStartUp-Monopod - C:\DOCUME~1\Kasutaja\LOCALS~1\Temp\b.exe
MSConfigStartUp-nvwins - C:\Program Files\Windows NT\nvwins.exe
MSConfigStartUp-PopRock - C:\DOCUME~1\Kasutaja\LOCALS~1\Temp\j.exe
AddRemove-help - C:\Program Files\Blitz3D\help\uninstall.exe
AddRemove-FIFA MANAGER 10 - C:\Program Files\EA SPORTS\FIFA MANAGER 10\eauninstall.exe
AddRemove-HTmov - C:\Program Files\HTmov\Uninstall.exe
AddRemove-HTviewer - C:\Program Files\HTviewer\Uninstall.exe
 
If combofix isn't on your desktop, please place move it there now so we can perform the following procedure.

1. Go to Start > Run > type Notepad.exe and click OK to open Notepad.
It must be Notepad, not Wordpad.
2. Copy the text in the below code box

Code:
File::
C:\WINDOWS\WSYS049.SYS
C:\WINDOWS\system32\03.tmp 
C:\WINDOWS\system32\013.tmp 
C:\WINDOWS\system32\0C.tmp 
C:\WINDOWS\system32\019.tmp 
C:\WINDOWS\system32\04.tmp


3. Go to the Notepad window and click Edit > Paste
4. Then click File > Save
5. Name the file CFScript.txt - Save the file to your Desktop
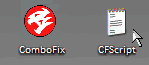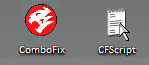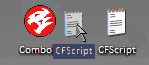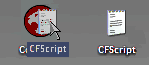
6. Then drag the CFScript (hold the left mouse button while dragging the file) and drop it (release the left mouse button) into ComboFix.exe as you see in the screenshot below. Important: Perform this instruction carefully!


CFScript-1.gif


ComboFix will begin to execute, just follow the prompts.
After reboot (in case it asks to reboot), it will produce a log for you.
Post that log (Combofix.txt) in your next reply.

Also please provide a fresh hiackthis log.
 
hijackthis log...
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
c:\Program Files\Microsoft Security Essentials\MsMpEng.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Google\Update\1.2.183.23\GoogleCrashHandler.exe
C:\WINDOWS\system32\CTsvcCDA.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\system32\PnkBstrA.exe
C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\wscntfy.exe
C:\WINDOWS\system32\notepad.exe
C:\WINDOWS\explorer.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Trend Micro\HiJackThis\HiJackThis.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.neti.ee/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: (no name) - {34123098-D81D-471D-AA97-37B110718A42} - C:\WINDOWS\system32\tuvVPhIB.dll (file missing)
O2 - BHO: WormRadar.com IESiteBlocker.NavFilter - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - (no file)
O2 - BHO: Windows Live Family Safety Browser Helper - {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - C:\Program Files\Windows Live\Family Safety\fssbho.dll
O2 - BHO: Click-to-Call BHO - {5C255C8A-E604-49b4-9D64-90988571CECB} - C:\Program Files\Windows Live\Messenger\wlchtc.dll
O2 - BHO: Search Helper - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: (no name) - {BA8FBC1F-CB33-46CA-BA88-48A3988ED988} - C:\WINDOWS\system32\byXPIyvW.dll (file missing)
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: Windows Live Toolbar Helper - {E15A8DC0-8516-42A1-81EA-DC94EC1ACF10} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: &Windows Live Toolbar - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O4 - HKLM\..\Run: [SoundMan] SOUNDMAN.EXE
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [CTCheck] C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [MSSE] "c:\Program Files\Microsoft Security Essentials\msseces.exe" -hide -runkey
O4 - HKCU\..\Run: [MsnMsgr] "C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe" /background
O4 - HKCU\..\Run: [DAEMON Tools Lite] "C:\Program Files\DAEMON Tools Lite\daemon.exe" -autorun
O4 - HKCU\..\Run: [EA Core] "C:\Program Files\Electronic Arts\EADM\Core.exe" -silent
O4 - HKCU\..\RunOnce: [Shockwave Updater] C:\WINDOWS\system32\Adobe\Shockwave 11\SwHelper_1150595.exe -Update -1150595 -"Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 5.1; FLV; .NET CLR 2.0.50727; .NET CLR 1.1.4322; .NET CLR 3.0.04506.30; .NET CLR 3.0.4506.2152; .NET CLR 3.5.30729; Creative ZENcast v2.00.13)" -"http://www.miniclip.com/games/world-soccer/en/"
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - Startup: OpenOffice.org 2.4.lnk = C:\Program Files\OpenOffice.org 2.4\program\quickstart.exe
O8 - Extra context menu item: Google Sidewiki... - res://C:\Program Files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_96D6FF0C6D236BF8.dll/cmsidewiki.html
O9 - Extra button: Blog This - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: &Blog This in Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {0CCA191D-13A6-4E29-B746-314DEE697D83} (Facebook Photo Uploader 5 Control) - http://upload.facebook.com/controls/2008.10.10_v5.5.8/FacebookPhotoUploader5.cab
O16 - DPF: {4BFD075D-C36E-4F28-BB0A-5D472795197A} (PowerLoader Class) - http://www.powerchallenge.com/applet/PowerLoader.cab
O16 - DPF: {4F1E5B1A-2A80-42CA-8532-2D05CB959537} (MSN Photo Upload Tool) - http://gfx1.hotmail.com/mail/w3/resources/MSNPUpld.cab
O16 - DPF: {6C269571-C6D7-4818-BCA4-32A035E8C884} (Creative Software AutoUpdate) - http://www.creative.com/softwareupdate/su/ocx/15101/CTSUEng.cab
O16 - DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} (Battlefield Heroes Updater) - https://www.battlefieldheroes.com/static/updater/BFHUpdater_4.0.21.0.cab
O16 - DPF: {917623D1-D8E5-11D2-BE8B-00104B06BDE3} (CamImage Class) - http://gw.tallinnlv.ee:11082/activex/AxisCamControl.cab
O16 - DPF: {EA6246B4-F380-443F-8727-9AEA3371146C} (CPlayFirstWeddingDashControl Object) - http://cdn.ll.neoedge.com/webgames/WeddingDash/WeddingDash.1.0.0.47.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/softwareupdate/su/ocx/15106/CTPID.cab
O18 - Protocol: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - (no file)
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O20 - Winlogon Notify: avgrsstarter - avgrsstx.dll (file missing)
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Creative Service for CDROM Access - Creative Technology Ltd - C:\WINDOWS\system32\CTsvcCDA.exe
O23 - Service: Google Update Service (gupdate) (gupdate) - Google Inc. - C:\Program Files\Google\Update\GoogleUpdate.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: PnkBstrA - Unknown owner - C:\WINDOWS\system32\PnkBstrA.exe
O23 - Service: Remote Procedure Call (HNM) (RPCER) - Unknown owner - C:\Program Files\Common Files\ODBC\comp.exe (file missing)

--
End of file - 8067 bytes
 
combofix log...
FILE ::
"c:\windows\system32\013.tmp"
"c:\windows\system32\019.tmp"
"c:\windows\system32\03.tmp"
"c:\windows\system32\04.tmp"
"c:\windows\system32\0C.tmp"
"c:\windows\WSYS049.SYS"
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

c:\windows\WSYS049.SYS
.
---- Previous Run -------
.
c:\documents and settings\Kasutaja\Application Data\bcrypt.html
c:\documents and settings\Kasutaja\Recent\Thumbs.db
c:\documents and settings\Kasutaja\Start Menu\Programs\Startup\MagicDisc.lnk
C:\Thumbs.db
c:\windows\Downloaded Program Files\f3initialsetup1.0.1.1.inf
c:\windows\Downloaded Program Files\popcaploader.inf
c:\windows\system32\28455546.exe
c:\windows\system32\BIhPVvut.ini
c:\windows\system32\BIhPVvut.ini2
c:\windows\system32\cfskbdka.ini
c:\windows\system32\fcvqvlxg.ini
c:\windows\system32\Thumbs.db
c:\windows\system32\WvyIPXyb.ini
c:\windows\system32\WvyIPXyb.ini2

.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.

-------\Legacy_6TO4
-------\Legacy_IAS
-------\Legacy_MYWEBSEARCHSERVICE
-------\Service_6to4
-------\Service_Ias
-------\Service_NETSVCS_0x0


((((((((((((((((((((((((( Files Created from 2010-03-26 to 2010-04-26 )))))))))))))))))))))))))))))))
.

2010-04-26 04:03 . 2010-04-26 04:03 388096 ----a-r- c:\documents and settings\Kasutaja\Application Data\Microsoft\Installer\{45A66726-69BC-466B-A7A4-12FCBA4883D7}\HiJackThis.exe
2010-04-26 04:03 . 2010-04-26 04:03 -------- d-----w- c:\program files\Trend Micro
2010-04-16 15:12 . 2010-04-16 15:13 -------- d-----w- c:\program files\Microsoft Security Essentials
2010-04-16 12:10 . 2010-04-16 12:10 503808 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\msvcp71.dll
2010-04-16 12:10 . 2010-04-16 12:10 499712 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\jmc.dll
2010-04-16 12:10 . 2010-04-16 12:10 348160 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\54\1a209876-64ac4a5e-n\msvcr71.dll
2010-04-16 12:10 . 2010-04-16 12:10 61440 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\17\6d0ad391-309a437f-n\decora-sse.dll
2010-04-16 12:10 . 2010-04-16 12:10 12800 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\Deployment\SystemCache\6.0\17\6d0ad391-309a437f-n\decora-d3d.dll
2010-04-16 12:10 . 2010-04-12 14:29 411368 ----a-w- c:\windows\system32\deployJava1.dll
2010-04-15 13:39 . 2010-04-15 13:39 -------- d-----w- C:\found.000

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-04-26 03:46 . 2008-11-12 19:38 -------- d-----w- c:\documents and settings\Kasutaja\Application Data\OpenOffice.org2
2010-04-25 17:04 . 2008-11-01 12:14 -------- d-----w- c:\program files\Malwarebytes' Anti-Malware
2010-04-25 15:54 . 2008-08-05 14:35 -------- d-----w- c:\documents and settings\Kasutaja\Application Data\uTorrent
2010-04-16 12:10 . 2008-08-07 20:24 -------- d-----w- c:\program files\Common Files\Java
2010-04-16 12:09 . 2008-08-07 20:25 -------- d-----w- c:\program files\Java
2010-04-16 11:44 . 2009-04-19 12:31 5918776 ----a-w- c:\documents and settings\All Users\Application Data\Malwarebytes\Malwarebytes' Anti-Malware\mbam-setup.exe
2010-04-16 11:40 . 2008-08-11 06:35 -------- d-----w- c:\documents and settings\All Users\Application Data\Avg8
2010-04-16 11:16 . 2008-10-14 19:58 -------- d-----w- c:\program files\Common Files\Apple
2010-03-30 16:06 . 2008-09-06 17:18 -------- d---a-w- c:\documents and settings\All Users\Application Data\TEMP
2010-03-29 12:24 . 2008-11-01 12:14 38224 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-03-29 12:24 . 2008-11-01 12:14 20824 ----a-w- c:\windows\system32\drivers\mbam.sys
2010-03-27 10:04 . 2008-08-05 14:35 -------- d-----w- c:\documents and settings\Kasutaja\Application Data\Sports Interactive
2010-03-24 20:38 . 2009-12-04 16:03 -------- d-----w- c:\program files\Death Rally
2010-03-21 22:25 . 2009-01-08 13:10 -------- d-----w- c:\program files\Safari
2010-03-21 22:21 . 2010-03-21 22:21 79144 ----a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.22.7\SetupAdmin.exe
2010-03-20 14:38 . 2010-03-20 14:38 -------- d-----w- c:\program files\Mozilla
2010-03-19 20:42 . 2008-08-18 12:00 -------- d-----w- c:\program files\uTorrent
2010-03-19 05:27 . 2008-12-01 12:32 -------- d-----w- c:\program files\GUNROX
2010-03-18 15:30 . 2008-08-07 20:12 -------- d-----w- c:\program files\Google
2010-03-18 14:54 . 2008-08-07 20:22 -------- d-----w- c:\program files\LimeWire
2010-03-18 14:53 . 2009-10-30 19:34 -------- d-----w- c:\program files\Glest_3.2.2
2010-03-18 14:52 . 2009-05-21 12:16 -------- d-----w- c:\documents and settings\All Users\Application Data\Electronic Arts
2010-03-18 14:52 . 2008-09-16 06:09 -------- d-----w- c:\program files\Electronic Arts
2010-03-18 14:50 . 2008-08-05 11:47 -------- d--h--w- c:\program files\InstallShield Installation Information
2010-03-18 14:42 . 2008-08-31 22:05 -------- d--h--w- c:\documents and settings\Kasutaja\Application Data\yahoo!
2010-03-18 14:42 . 2008-08-31 19:13 -------- d-----w- c:\documents and settings\All Users\Application Data\Yahoo!
2010-03-18 14:41 . 2008-08-31 13:02 -------- d-----w- c:\program files\AIM
2010-03-18 14:41 . 2008-08-31 13:03 -------- d-----w- c:\documents and settings\Kasutaja\Application Data\Aim
2010-03-15 04:56 . 2008-11-07 05:12 -------- d-----w- c:\program files\Eidos Interactive
2010-03-11 21:56 . 2008-11-12 19:40 1 ----a-w- c:\documents and settings\Kasutaja\Application Data\OpenOffice.org2\user\uno_packages\cache\stamp.sys
2010-03-10 13:52 . 2009-09-04 14:54 69 ----a-w- c:\documents and settings\Kasutaja\jagex_runescape_preferences2.dat
2010-03-10 13:50 . 2008-10-03 12:30 41 ----a-w- c:\documents and settings\Kasutaja\jagex_runescape_preferences.dat
2010-03-10 13:30 . 2008-11-21 22:00 -------- d-----w- c:\program files\EA SPORTS
2010-03-09 17:44 . 2009-01-20 17:19 -------- d-----w- c:\documents and settings\All Users\Application Data\Sports Interactive
2010-03-08 18:46 . 2009-07-14 12:11 -------- d-----w- c:\program files\Sports Interactive
2010-03-08 09:25 . 2009-03-01 15:02 -------- d-----w- c:\documents and settings\Kasutaja\Application Data\U3
2010-03-07 11:05 . 2010-03-07 11:05 -------- d-----w- c:\program files\GDS
2010-02-27 06:54 . 2009-06-17 07:17 -------- d-----w- c:\program files\Rockstar Games
2010-02-25 17:07 . 2010-02-25 17:05 43520 ----a-w- c:\windows\system32\CmdLineExt03.dll
2010-02-20 19:22 . 2009-09-24 04:48 24104 ----a-w- c:\windows\system32\GDIPFONTCACHEV1.DAT
2010-02-16 14:43 . 2010-02-16 14:43 79144 ----a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.21.10\SetupAdmin.exe
2010-02-05 16:28 . 2009-12-05 16:57 79488 ----a-w- c:\documents and settings\Kasutaja\Application Data\Sun\Java\jre1.6.0_17\gtapi.dll
2009-07-14 00:16 . 2009-07-14 00:16 1044480 ----a-w- c:\program files\mozilla firefox\plugins\libdivx.dll
2009-07-14 00:16 . 2009-07-14 00:16 200704 ----a-w- c:\program files\mozilla firefox\plugins\ssldivx.dll
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{34123098-D81D-471D-AA97-37B110718A42}]
c:\windows\system32\tuvVPhIB.dll [BU]

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{BA8FBC1F-CB33-46CA-BA88-48A3988ED988}]
c:\windows\system32\byXPIyvW.dll [BU]

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"MsnMsgr"="c:\program files\Windows Live\Messenger\MsnMsgr.Exe" [2009-07-26 3883856]
"DAEMON Tools Lite"="c:\program files\DAEMON Tools Lite\daemon.exe" [2008-12-29 687560]
"EA Core"="c:\program files\Electronic Arts\EADM\Core.exe" [BU]

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\RunOnce]
"Shockwave Updater"="c:\windows\system32\Adobe\Shockwave 11\SwHelper_1150595.exe" [2009-03-19 460216]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SoundMan"="SOUNDMAN.EXE" [2006-11-17 577536]
"SunJavaUpdateSched"="c:\program files\Common Files\Java\Java Update\jusched.exe" [2010-02-18 248040]
"CTCheck"="c:\program files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe" [2007-11-06 397312]
"QuickTime Task"="c:\program files\QuickTime\qttask.exe" [2009-05-26 413696]
"MSSE"="c:\program files\Microsoft Security Essentials\msseces.exe" [2010-02-21 1093208]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360]

c:\documents and settings\Kasutaja\Start Menu\Programs\Startup\
OpenOffice.org 2.4.lnk - c:\program files\OpenOffice.org 2.4\program\quickstart.exe [2008-5-30 393216]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\avgrsstarter]
avgrsstx.dll [BU]

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\MsMpSvc]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\EnableDCOM]
N [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\restrictanonymous]
 [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\restrictanonymoussam]
 [X]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2008-06-11 23:38 34672 ----a-w- c:\program files\Adobe\Reader 9.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\AVG8_TRAY]
2008-11-28 07:31 1261336 ----a-w- c:\progra~1\AVG\AVG8\avgtray.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\CTSyncU.exe]
2007-07-17 08:03 868352 ------w- c:\program files\Creative\Sync Manager Unicode\CTSyncU.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Fast Encoder]
c:\docume~1\Kasutaja\LOCALS~1\Temp\fedhost.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\fssui]
2009-08-05 19:48 647520 ----a-w- c:\program files\Windows Live\Family Safety\fsui.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\hivew]
c:\docume~1\Kasutaja\LOCALS~1\Temp\281709843050don.dll [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\iTunesHelper]
2008-11-20 11:20 290088 ----a-w- c:\program files\iTunes\iTunesHelper.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Java Runtime Enviornment]
c:\windows\TEMP\c:\windows\TEMP\Update.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\MicrosoftUpdate]
c:\documents and settings\Kasutaja\Application Data\taskeng.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Monopod]
c:\docume~1\Kasutaja\LOCALS~1\Temp\b.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\nvwins]
c:\program files\Windows NT\nvwins.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\PopRock]
c:\docume~1\Kasutaja\LOCALS~1\Temp\j.exe [BU]

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\services]
"Bonjour Service"=2 (0x2)
"avg8wd"=2 (0x2)
"avg8emc"=2 (0x2)

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\AVG\\AVG8\\avgemc.exe"=
"c:\\Program Files\\AVG\\AVG8\\avgupd.exe"=
"c:\\Program Files\\uTorrent\\uTorrent.exe"=
"c:\\Documents and Settings\\Kasutaja\\My Documents\\LimeWire\\Saved\\Command & Conquer Generals\\game.dat"=
"c:\\Program Files\\SecondLife\\SLVoice.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\EA GAMES\\Command & Conquer Generals Zero Hour\\game.dat"=
"c:\\WINDOWS\\system32\\PnkBstrA.exe"=
"c:\\WINDOWS\\system32\\PnkBstrB.exe"=
"c:\\Program Files\\EA GAMES\\Command and Conquer Generals\\game.dat"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Java\\jre6\\bin\\java.exe"=
"c:\\Program Files\\EA GAMES\\Command and Conquer Generals\\patchget.dat"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Sync\\WindowsLiveSync.exe"=
"c:\\Program Files\\Skype\\Plugin Manager\\skypePM.exe"=
"c:\\Program Files\\Skype\\Phone\\Skype.exe"=
"c:\\Documents and Settings\\Owner\\My Documents\\Downloads\\cnc\\Command And Conquer - Tiberian Sun + Firestorm Expansion\\game.exe"=
"c:\\Program Files\\Sports Interactive\\Football Manager 2010\\fm.exe"=

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"1806:TCP"= 1806:TCP:eghxgmt

R3 PbsAuDrv;PolderbitS Audio Driver;c:\windows\system32\drivers\pbsaudrv.sys [20.12.2009 13:25 110752]
R3 seehcri;Sony Ericsson seehcri Device Driver;c:\windows\system32\drivers\seehcri.sys [25.11.2009 22:10 27632]
S0 sptd;sptd;c:\windows\system32\drivers\sptd.sys [10.03.2009 0:08 717296]
S2 ghkclv;Server Manager;c:\windows\system32\svchost.exe -k netsvcs [28.02.2006 15:00 14336]
S2 gupdate;Google Update Service (gupdate);c:\program files\Google\Update\GoogleUpdate.exe [21.12.2009 17:18 135664]
S2 RPCER;Remote Procedure Call (HNM);c:\program files\Common Files\ODBC\comp.exe --> c:\program files\Common Files\ODBC\comp.exe [?]
S3 kzixj;kzixj;\??\c:\windows\system32\03.tmp --> c:\windows\system32\03.tmp [?]
S3 liulu;liulu;\??\c:\windows\system32\013.tmp --> c:\windows\system32\013.tmp [?]
S3 ntcexkd;ntcexkd;\??\c:\windows\system32\0C.tmp --> c:\windows\system32\0C.tmp [?]
S3 qtdtknoxf;qtdtknoxf;\??\c:\windows\system32\019.tmp --> c:\windows\system32\019.tmp [?]
S3 s0016bus;Sony Ericsson Device 0016 driver (WDM);c:\windows\system32\drivers\s0016bus.sys [25.11.2009 22:06 89256]
S3 s0016mdfl;Sony Ericsson Device 0016 USB WMC Modem Filter;c:\windows\system32\drivers\s0016mdfl.sys [25.11.2009 22:06 15016]
S3 s0016mdm;Sony Ericsson Device 0016 USB WMC Modem Driver;c:\windows\system32\drivers\s0016mdm.sys [25.11.2009 22:06 120744]
S3 s0016mgmt;Sony Ericsson Device 0016 USB WMC Device Management Drivers (WDM);c:\windows\system32\drivers\s0016mgmt.sys [25.11.2009 22:06 114216]
S3 s0016nd5;Sony Ericsson Device 0016 USB Ethernet Emulation SEMC0016 (NDIS);c:\windows\system32\drivers\s0016nd5.sys [25.11.2009 22:06 25512]
S3 s0016obex;Sony Ericsson Device 0016 USB WMC OBEX Interface;c:\windows\system32\drivers\s0016obex.sys [25.11.2009 22:06 110632]
S3 s0016unic;Sony Ericsson Device 0016 USB Ethernet Emulation SEMC0016 (WDM);c:\windows\system32\drivers\s0016unic.sys [25.11.2009 22:06 115752]
S3 txddrdm;txddrdm;\??\c:\windows\system32\04.tmp --> c:\windows\system32\04.tmp [?]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
getPlusHelper REG_MULTI_SZ getPlusHelper

HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs
NETSVCS_0x1
NETSVCS_0x2
NETSVCS_0x3
NETSVCS_0x4
NETSVCS_0x5
NETSVCS_0x6
NETSVCS_0x7
NETSVCS_0x8
NETSVCS_0x9
NETSVCS_0xa
NETSVCS_0xb
ghkclv
.
Contents of the 'Scheduled Tasks' folder

2010-04-26 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files\Google\Update\GoogleUpdate.exe [2009-12-21 14:18]

2010-04-26 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files\Google\Update\GoogleUpdate.exe [2009-12-21 14:18]

2010-04-26 c:\windows\Tasks\MP Scheduled Scan.job
- c:\program files\Microsoft Security Essentials\MpCmdRun.exe [2009-12-09 15:02]
.
.
------- Supplementary Scan -------
.
uStart Page = hxxp://www.neti.ee/
IE: Google Sidewiki... - c:\program files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_96D6FF0C6D236BF8.dll/cmsidewiki.html
DPF: {4BFD075D-C36E-4F28-BB0A-5D472795197A} - hxxp://www.powerchallenge.com/applet/PowerLoader.cab
DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} - hxxps://www.battlefieldheroes.com/static/updater/BFHUpdater_4.0.21.0.cab
FF - ProfilePath - c:\documents and settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\
FF - plugin: c:\documents and settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\extensions\{E2883E8F-472F-4fb0-9522-AC9BF37916A7}\plugins\np_gp.dll
FF - plugin: c:\documents and settings\Kasutaja\Application Data\Mozilla\Firefox\Profiles\rzne5otf.default\extensions\[email protected]\platform\WINNT_x86-msvc\plugins\npBFHUpdater.dll
FF - plugin: c:\documents and settings\Kasutaja\My Documents\DivX\DivX Player\npDivxPlayerPlugin.dll
FF - plugin: c:\documents and settings\Kasutaja\My Documents\DivX\DivX Web Player\npdivx32.dll
FF - plugin: c:\program files\Google\Update\1.2.183.23\npGoogleOneClick8.dll
FF - plugin: c:\program files\Mozilla Firefox\plugins\npdeployJava1.dll
FF - plugin: c:\program files\Mozilla Firefox\plugins\NPOP7PlugIn.dll
FF - plugin: c:\program files\Windows Live\Photo Gallery\NPWLPG.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\

---- FIREFOX POLICIES ----
c:\program files\Mozilla Firefox\greprefs\all.js - pref("ui.use_native_colors", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("ui.use_native_popup_windows", false);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.enable_click_image_resizing", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("accessibility.browsewithcaret_shortcut.enabled", true);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("javascript.options.mem.high_water_mark", 32);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("javascript.options.mem.gc_frequency", 1600);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.auth.force-generic-ntlm", false);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("svg.smil.enabled", false);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("ui.trackpoint_hack.enabled", -1);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.debug", false);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.agedWeight", 2);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.bucketSize", 1);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.maxTimeGroupings", 25);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.timeGroupingSize", 604800);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.boundaryWeight", 25);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.formfill.prefixWeight", 5);
c:\program files\Mozilla Firefox\greprefs\all.js - pref("html5.enable", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("app.update.download.backgroundInterval", 600);
c:\program files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("app.update.url.manual", "http://www.firefox.com");
c:\program files\Mozilla Firefox\defaults\pref\firefox-branding.js - pref("browser.search.param.yahoo-fr-ja", "mozff");
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.name", "chrome://browser/locale/browser.properties");
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.description", "chrome://browser/locale/browser.properties");
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add", "addons.mozilla.org");
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add.36", "getpersonas.com");
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("lightweightThemes.update.enabled", true);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.allTabs.previews", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("plugins.hide_infobar_for_outdated_plugin", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("plugins.update.notifyUser", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("toolbar.customization.usesheet", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.enable", false);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.max", 20);
c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.cachetime", 20);
.

**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-04-26 19:00
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes ...

scanning hidden autostart entries ...

scanning hidden files ...

scan completed successfully
hidden files: 0

**************************************************************************

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\kzixj]
"ImagePath"="\??\c:\windows\system32\03.tmp"

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\liulu]
"ImagePath"="\??\c:\windows\system32\013.tmp"

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\ntcexkd]
"ImagePath"="\??\c:\windows\system32\0C.tmp"

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\qtdtknoxf]
"ImagePath"="\??\c:\windows\system32\019.tmp"

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\txddrdm]
"ImagePath"="\??\c:\windows\system32\04.tmp"

[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\ghkclv]
"ServiceDll"="c:\windows\system32\nzixtmk.dll"
.
--------------------- LOCKED REGISTRY KEYS ---------------------

[HKEY_USERS\S-1-5-21-854245398-1957994488-682003330-1004\Software\SecuROM\!CAUTION! NEVER A OR CHANGE ANY KEY*]
"??"=hex:b5,d2,7c,22,9b,7f,e9,ea,6b,d9,5f,f9,44,22,10,19,f4,64,ae,d1,39,7c,4d,
d4,69,c4,3c,de,03,a6,63,ba,9e,2d,44,e8,c7,32,3f,a0,8b,5c,19,18,68,0e,da,eb,\
"??"=hex:a5,34,05,48,cc,09,e0,e2,b6,5c,f3,c3,09,cb,b6,93

[HKEY_USERS\S-1-5-21-854245398-1957994488-682003330-1004\Software\SecuROM\License information*]
"datasecu"=hex:84,b4,77,1a,43,db,cd,0e,6b,ce,38,64,80,7a,bf,39,02,3a,22,e5,9f,
0d,ac,e7,6a,93,7b,66,b6,74,62,17,47,81,d0,cd,c2,2d,3a,e1,d7,e3,dd,d4,69,9c,\
"rkeysecu"=hex:82,f9,0d,d7,15,7a,20,1f,ff,b5,c2,81,40,fd,09,8d
.
Completion time: 2010-04-26 19:04:56
ComboFix-quarantined-files.txt 2010-04-26 16:04

Pre-Run: 12*764*270*592 bytes free
Post-Run: 12*732*461*056 bytes free

- - End Of File - - C8F341246B14F52E122248A1010BA74C
 
Ok, lets abandon combofix for a little bit and lets run Malwarebytes and Superantispyware.

Make sure malwarebytes is fully updated before running. When its done please post the logfile that it created.

When done please go here to download superantispyware and run it after you update it.

http://download.cnet.com/SuperAntiSpyware-Free-Edition/3000-8022_4-10523889.html

To view the log, open superantispyware, click on the preferences button and then the statistics/logs tab and open the log you just created, then copy and paste that log back here.

When you come back to reply, please post logs from

Malwarebytes
Superantispyware
Fresh hijackthis
 
hijackthis log..
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
c:\Program Files\Microsoft Security Essentials\MsMpEng.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Google\Update\1.2.183.23\GoogleCrashHandler.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\CTsvcCDA.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\system32\PnkBstrA.exe
C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\SOUNDMAN.EXE
C:\Program Files\Common Files\Java\Java Update\jusched.exe
C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe
C:\Program Files\Microsoft Security Essentials\msseces.exe
C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe
C:\Program Files\DAEMON Tools Lite\daemon.exe
C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Program Files\OpenOffice.org 2.4\program\soffice.exe
C:\Program Files\OpenOffice.org 2.4\program\soffice.BIN
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Trend Micro\HiJackThis\HiJackThis.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.neti.ee/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: (no name) - {34123098-D81D-471D-AA97-37B110718A42} - C:\WINDOWS\system32\tuvVPhIB.dll (file missing)
O2 - BHO: WormRadar.com IESiteBlocker.NavFilter - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - (no file)
O2 - BHO: Windows Live Family Safety Browser Helper - {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - C:\Program Files\Windows Live\Family Safety\fssbho.dll
O2 - BHO: Click-to-Call BHO - {5C255C8A-E604-49b4-9D64-90988571CECB} - C:\Program Files\Windows Live\Messenger\wlchtc.dll
O2 - BHO: Search Helper - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: (no name) - {BA8FBC1F-CB33-46CA-BA88-48A3988ED988} - C:\WINDOWS\system32\byXPIyvW.dll (file missing)
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: Windows Live Toolbar Helper - {E15A8DC0-8516-42A1-81EA-DC94EC1ACF10} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: &Windows Live Toolbar - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O4 - HKLM\..\Run: [SoundMan] SOUNDMAN.EXE
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [CTCheck] C:\Program Files\Creative\Creative ZEN\ZEN Media Explorer\CTCheck.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [MSSE] "c:\Program Files\Microsoft Security Essentials\msseces.exe" -hide -runkey
O4 - HKCU\..\Run: [MsnMsgr] "C:\Program Files\Windows Live\Messenger\MsnMsgr.Exe" /background
O4 - HKCU\..\Run: [DAEMON Tools Lite] "C:\Program Files\DAEMON Tools Lite\daemon.exe" -autorun
O4 - HKCU\..\Run: [EA Core] "C:\Program Files\Electronic Arts\EADM\Core.exe" -silent
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKCU\..\RunOnce: [Shockwave Updater] C:\WINDOWS\system32\Adobe\Shockwave 11\SwHelper_1150595.exe -Update -1150595 -"Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 5.1; FLV; .NET CLR 2.0.50727; .NET CLR 1.1.4322; .NET CLR 3.0.04506.30; .NET CLR 3.0.4506.2152; .NET CLR 3.5.30729; Creative ZENcast v2.00.13)" -"http://www.miniclip.com/games/world-soccer/en/"
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - Startup: OpenOffice.org 2.4.lnk = C:\Program Files\OpenOffice.org 2.4\program\quickstart.exe
O8 - Extra context menu item: Google Sidewiki... - res://C:\Program Files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_96D6FF0C6D236BF8.dll/cmsidewiki.html
O9 - Extra button: Blog This - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: &Blog This in Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: @C:\Program Files\Messenger\Msgslang.dll,-61144 - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {0CCA191D-13A6-4E29-B746-314DEE697D83} (Facebook Photo Uploader 5 Control) - http://upload.facebook.com/controls/2008.10.10_v5.5.8/FacebookPhotoUploader5.cab
O16 - DPF: {4BFD075D-C36E-4F28-BB0A-5D472795197A} (PowerLoader Class) - http://www.powerchallenge.com/applet/PowerLoader.cab
O16 - DPF: {4F1E5B1A-2A80-42CA-8532-2D05CB959537} (MSN Photo Upload Tool) - http://gfx1.hotmail.com/mail/w3/resources/MSNPUpld.cab
O16 - DPF: {6C269571-C6D7-4818-BCA4-32A035E8C884} (Creative Software AutoUpdate) - http://www.creative.com/softwareupdate/su/ocx/15101/CTSUEng.cab
O16 - DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} (Battlefield Heroes Updater) - https://www.battlefieldheroes.com/static/updater/BFHUpdater_4.0.21.0.cab
O16 - DPF: {917623D1-D8E5-11D2-BE8B-00104B06BDE3} (CamImage Class) - http://gw.tallinnlv.ee:11082/activex/AxisCamControl.cab
O16 - DPF: {EA6246B4-F380-443F-8727-9AEA3371146C} (CPlayFirstWeddingDashControl Object) - http://cdn.ll.neoedge.com/webgames/WeddingDash/WeddingDash.1.0.0.47.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/softwareupdate/su/ocx/15106/CTPID.cab
O18 - Protocol: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - (no file)
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O20 - Winlogon Notify: !SASWinLogon - C:\Program Files\SUPERAntiSpyware\SASWINLO.dll
O20 - Winlogon Notify: avgrsstarter - avgrsstx.dll (file missing)
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Creative Service for CDROM Access - Creative Technology Ltd - C:\WINDOWS\system32\CTsvcCDA.exe
O23 - Service: Google Update Service (gupdate) (gupdate) - Google Inc. - C:\Program Files\Google\Update\GoogleUpdate.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: PnkBstrA - Unknown owner - C:\WINDOWS\system32\PnkBstrA.exe
O23 - Service: Remote Procedure Call (HNM) (RPCER) - Unknown owner - C:\Program Files\Common Files\ODBC\comp.exe (file missing)

--
End of file - 8699 bytes
 
superantispyware log...
Memory items scanned : 470
Memory threats detected : 0
Registry items scanned : 5031
Registry threats detected : 8
File items scanned : 40068
File threats detected : 246

Adware.Tracking Cookie
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornowithteen[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@oddcast[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@need-xxx[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@ideal-teens[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@www.****maturewoman[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@yadro[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adinterax[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornhost[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected]****[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@****meplz[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@xxx-spoof[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@casualteensex[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adultstats[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@homepornvideotube[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@chupateens[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@nastyteensdesire[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@mysister****ed[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@****erville[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@xxxcounter[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@xxxbabesparadise[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@doubleclick[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@****[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sexyminks[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@statcounter[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hisexgirls[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@cleoteener[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tsprotraffic[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sex9[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@zedo[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@specificclick[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@warez2u[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@newpornmovies[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hardsextubepremium[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornopur[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@atwola[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@flash-porn[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@www.****erville[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@famouspornstars[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sexlist[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hardsextube[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@crazyhomesex[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected]****ed[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adultfriendfinder[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@naked-pornstars[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adprotraffic[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected]****[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@glamoursexladys[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@myroitracking[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@clicksor[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@aged****s[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sexvideomix[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@elgirlsex[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sextracker[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@toplist[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@teensporn[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected]****s[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@intersexxx[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@teenexgirlfriends[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adultsex[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@atdmt[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tradedoubler[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@3maturesex[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@freshxxxtube[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@toplist[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pro-market[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adultxpix[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@****maturewoman[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@teeniesmile[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornbitches[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hornymatches[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@revsci[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@ero-advertising[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@mywebsearch[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@legendarypornmovies[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@greatteengirl[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tubesexclips[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@russianpornoxxx[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@rambler[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@18pornmovies[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornosphere[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@trafficmp[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@discounts2009[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@www.****[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@teenshowtime[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@blondesexy[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@chitika[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@invitemedia[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tubesexmovies[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@yourpornvids[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tacoda[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sexytgp[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@apmebf[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@1800banners[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@idealsexy[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adtech[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@myadultclips[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@porn-ad[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@daywithapornstar[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adbrite[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@tribalfusion[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@fullsexmovies[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@serving-sys[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@advertising[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@trafficregenerator[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@sexudar[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@insightexpressai[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@clipadulte[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@abyssteens[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@maniaporno[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@imrworldwide[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@excellentsextube[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@adultadworld[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@playthis****[3].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hitbox[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@babesteenagers[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][3].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@pornstartale[1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@hqsextube[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@interclick[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@babelovesex[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@overture[2].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@collective-media[1].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][1].txt
C:\Documents and Settings\Kasutaja\Cookies\kasutaja@media6degrees[2].txt
C:\Documents and Settings\Kasutaja\Cookies\[email protected][2].txt
C:\Vana HDD\Documents and Settings\Owner\Cookies\[email protected][1].txt
C:\Vana HDD\Documents and Settings\Owner\Cookies\owner@accounts[2].txt
C:\Vana HDD\Documents and Settings\Owner\Cookies\[email protected][1].txt
C:\Vana HDD\Documents and Settings\Owner\Cookies\[email protected][2].txt
C:\Vana HDD\Documents and Settings\Owner\Local Settings\Temp\Cookies\owner@clicktorrent[1].txt
C:\Vana HDD\Documents and Settings\Owner\Local Settings\Temp\Cookies\owner@apmebf[1].txt

Rogue.Component/Trace
HKLM\Software\Microsoft\4826EDEF
HKLM\Software\Microsoft\4826EDEF#4826edef
HKLM\Software\Microsoft\4826EDEF#Version
HKLM\Software\Microsoft\4826EDEF#red_srv
HKLM\Software\Microsoft\4826EDEF#red_srv_bckp
HKLM\Software\Microsoft\4826EDEF#4826406f
HKLM\Software\Microsoft\4826EDEF#4826298a

Trojan.Fake-Alert/Trace
HKU\S-1-5-21-854245398-1957994488-682003330-1004\SOFTWARE\Microsoft\fias4013

Trojan.Agent/Gen-Krpytik
C:\PROGRAM FILES\ELECTRONIC ARTS\RED ALERT 3\RLD-RA3K.EXE
 
malewarebytes log...
Scan type: Full scan (C:\|)
Objects scanned: 361357
Time elapsed: 3 hour(s), 23 minute(s), 31 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 0
Registry Values Infected: 0
Registry Data Items Infected: 0
Folders Infected: 0
Files Infected: 0

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
(No malicious items detected)

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
(No malicious items detected)

Folders Infected:
(No malicious items detected)

Files Infected:
(No malicious items detected)
 
Ok, lets start off by cleaning up your hijackthis log.

Rerun hijackthis and place a check next to these entries.

O2 - BHO: (no name) - {34123098-D81D-471D-AA97-37B110718A42} - C:\WINDOWS\system32\tuvVPhIB.dll (file missing)
O2 - BHO: WormRadar.com IESiteBlocker.NavFilter - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - (no file)
O2 - BHO: (no name) - {BA8FBC1F-CB33-46CA-BA88-48A3988ED988} - C:\WINDOWS\system32\byXPIyvW.dll (file missing)
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKCU\..\RunOnce: [Shockwave Updater] C:\WINDOWS\system32\Adobe\Shockwave 11\SwHelper_1150595.exe -Update -1150595 -"Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 5.1; FLV; .NET CLR 2.0.50727; .NET CLR 1.1.4322; .NET CLR 3.0.04506.30; .NET CLR 3.0.4506.2152; .NET CLR 3.5.30729; Creative ZENcast v2.00.13)" -"http://www.miniclip.com/games/world-soccer/en/"
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - Startup: OpenOffice.org 2.4.lnk = C:\Program Files\OpenOffice.org 2.4\program\quickstart.exe
O18 - Protocol: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - (no file)
O20 - Winlogon Notify: avgrsstarter - avgrsstx.dll (file missing)

Then click on fix checked at the bottom.

Please provide me with an uninstall list using hijackthis. Open hijackthis and click on open misc tools section, click on open uninstall manager, click on save, save the file and then copy and paste that log back here.

If you haven't already done so please download ccleaner and check the options that are listed in the attached image then click on run cleaner.

Now please delete the current version of combofix you have and download the latest version and run it and post the log.

http://download.bleepingcomputer.com/sUBs/ComboFix.exe
 

Attachments

  • ccleaner.JPG
    ccleaner.JPG
    76.3 KB · Views: 378
how can i uninstall combofix?
ive done all, save the hijackthis uninstall log and cheked the stuff, i just go stuck in ununstalling combofix.
i just coulnt find the place.
 
Back
Top